
Choosing Between OAuth and API Key for Org-Wide Authentication
Decide whether to authorize the connector by signing in as an administrator, or by supplying an API key from the business application.
Table 1. OAuth compared with API key
| OAuth | API key | |
|---|---|---|
| How you authorize | Sign in to the business application as a System Administrator and grant permissions. | Generate a key in the business application and enter it in the connector. |
| What is stored | A refresh token, held in the per-tenant vault. | The API key. |
| Renewal | Tokens refresh automatically. Reauthorize if permissions change. | Replace the key when it is rotated or revoked. |
| Requires an administrator | Yes, at the time of authorization. | Only to generate the key. |
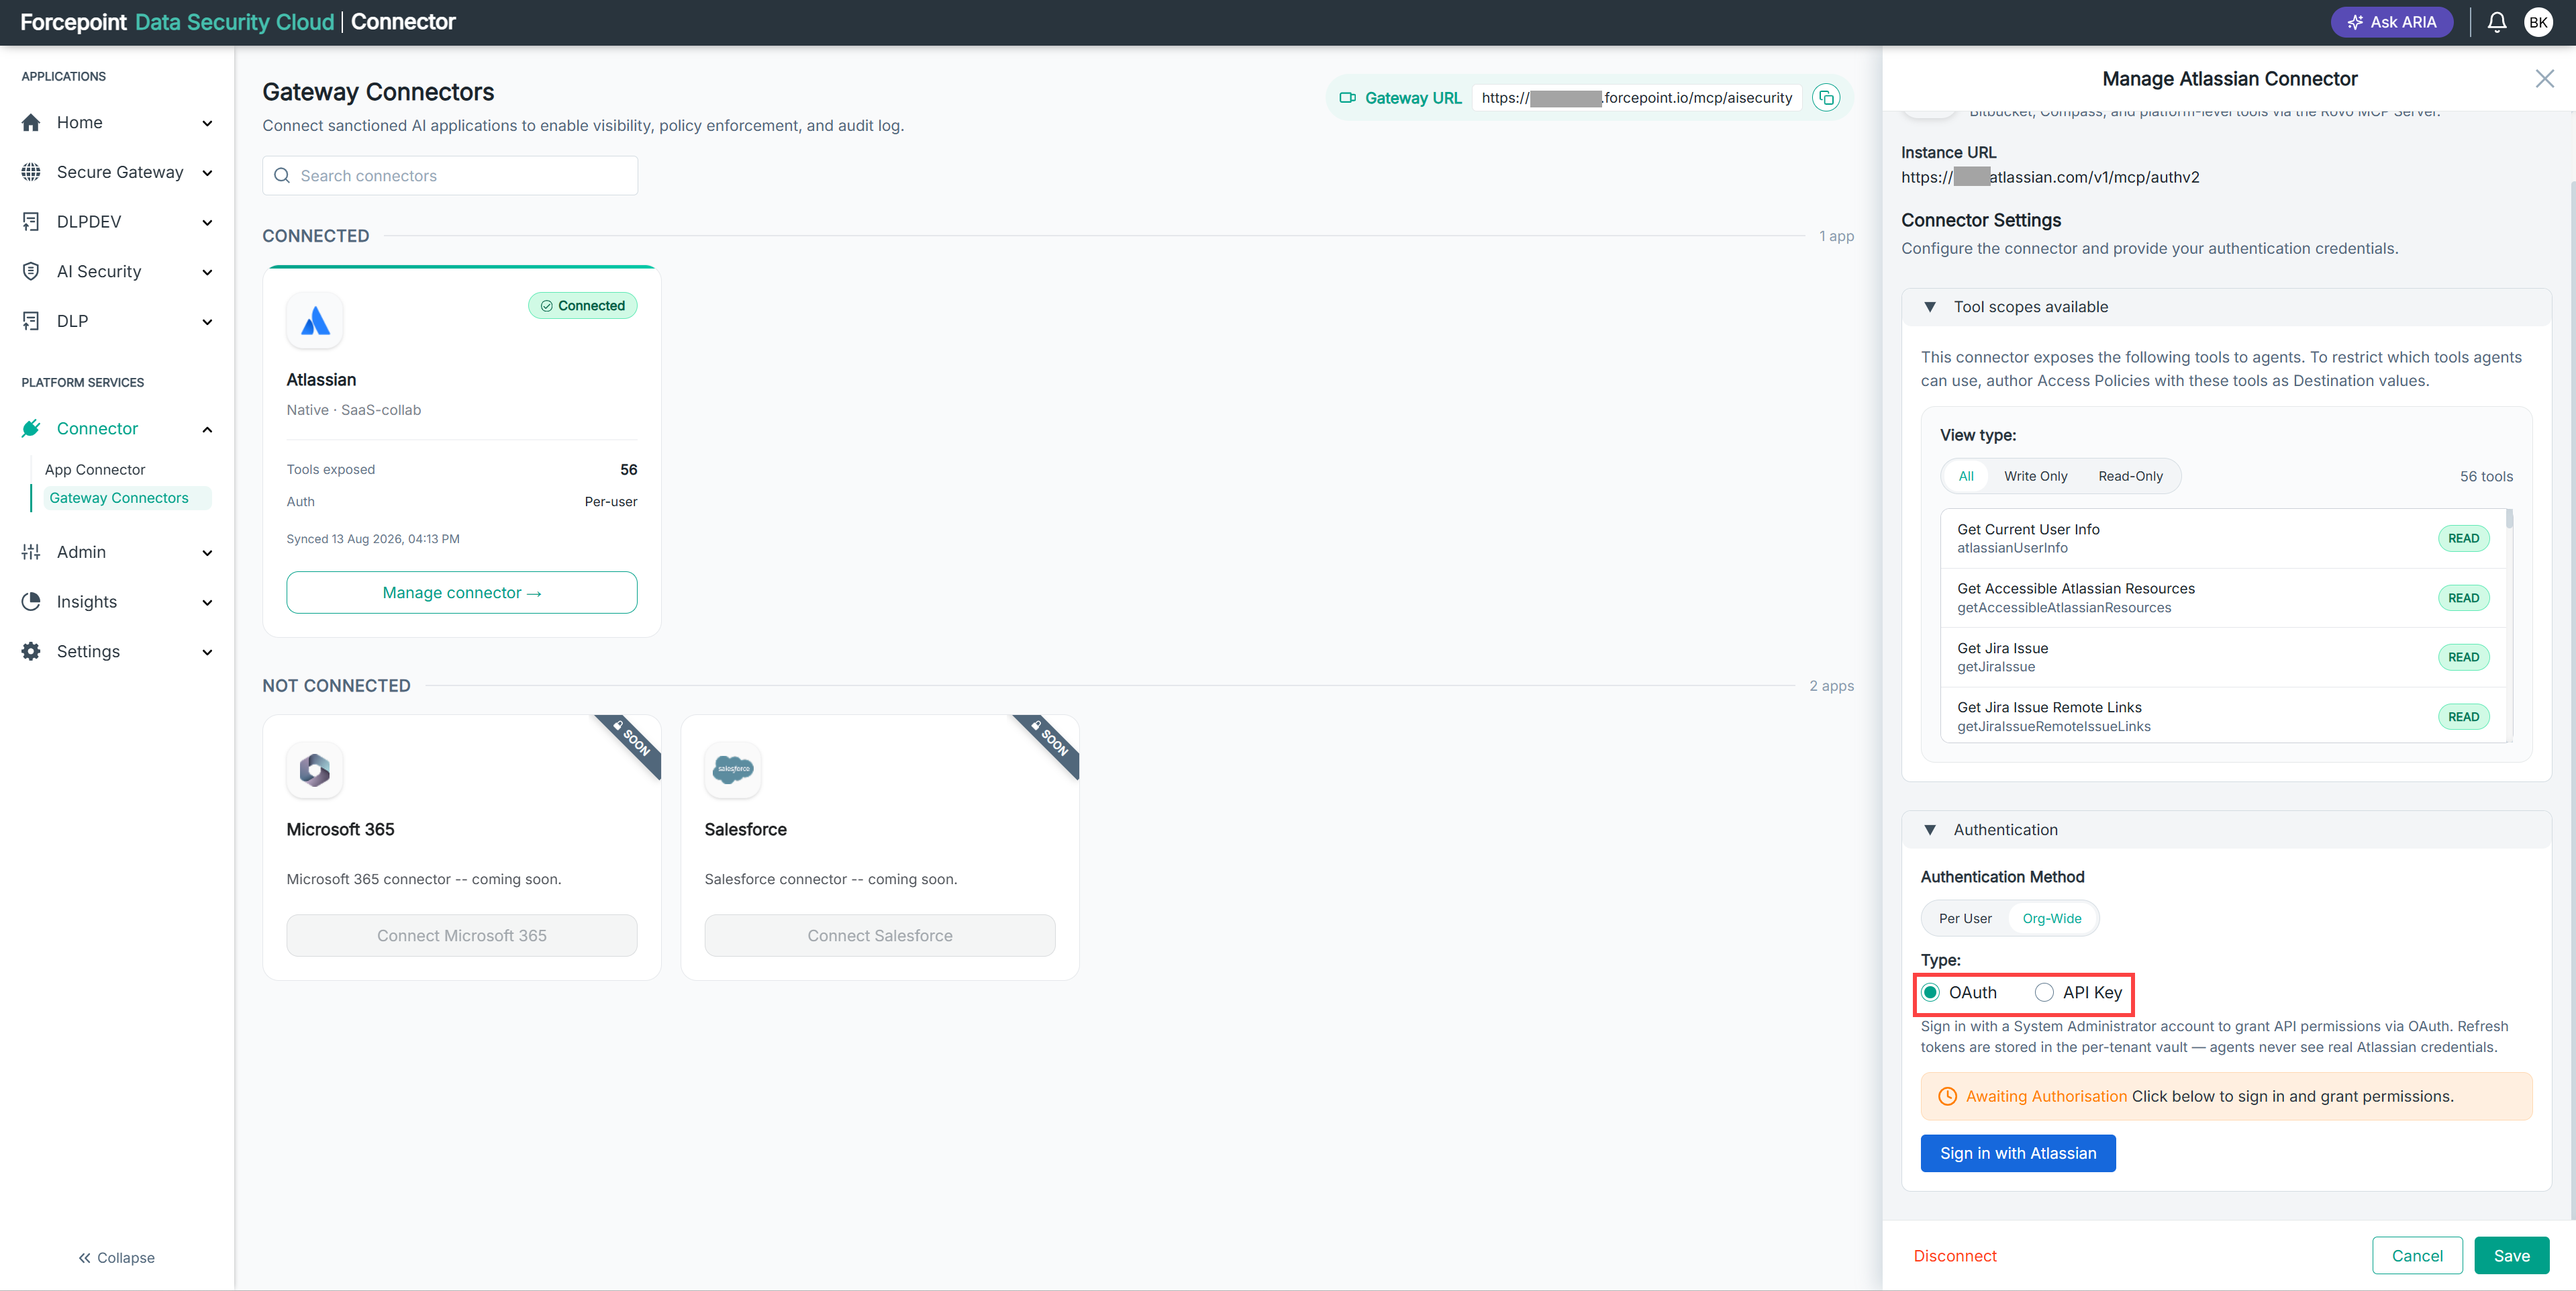
With either type, AI Security holds the credential. Your agents never see the real credentials for the business application.
Steps
- Determine whether a System Administrator is available to authorize the connector.
- Determine whether your organization prefers to manage API keys or delegated permissions.
- Select the type that matches.
Result
You know which authorization type to configure on the connector.