After uploading and validating DPS license JSON, you can select Forcepoint DLP data pattern from the Data Patterns section while configuring API scanning of files for any of the following supported applications:
- Microsoft 365
- Google Workspace
- Salesforce
- ServiceNow
- Box
- Dropbox
- AWS S3
- Cisco Webex
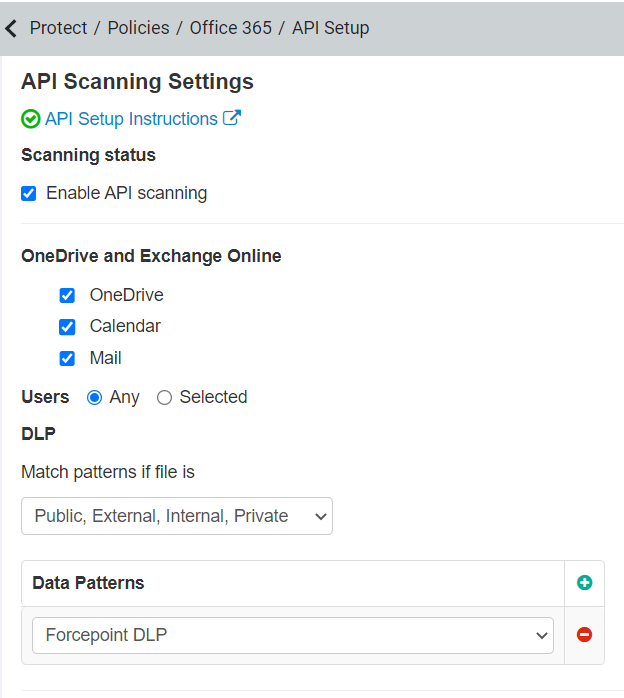
Forcepoint DLP currently supports scanning of File objects for API Scanning.
While configuring the application, you can select only Anti-malware data patterns that you have purchased as part of Forcepoint ONE SSE subscription along with the Forcepoint DLP data pattern. You can find the Anti-malware data patterns in the page.
For all the FSM-based policies, Forcepoint ONE SSE executes the action returned by Forcepoint DLP.
Forcepoint ONE SSE recommends you to create the following API policies if alerts and Policy ID in API Audit logs are needed for FSM-based policy:
- A policy with Anti-malware data pattern with any actions and alerting
- Another policy with the Forcepoint DLP data pattern set to Allow action placed at bottom of all configured policies
If an action is returned by both the FSM-based policy (with Forcepoint DLP data pattern) and another API policy (with Anti-malware data pattern) in Forcepoint ONE SSE, the most severe action is enforced. The actions are prioritized from most severe to least severe, with the most severe at the top of the list:
- Quarantine
- Remove All Sharing
- Remove Public+External Sharing
- Remove Public Sharing
- Encrypt
- CreateCopy
- Allow/Alert
Using FSM-based policy with Forcepoint ONE SSE API policy together might result in FSM incidents displaying incorrect action details. To determine the actual action implemented, refer to the Forcepoint ONE SSE API logs.