Content migration in progress, completing by midnight IST on 17 November 2026.
Steps to add an FSM application based on FSM template.
Steps
-
In the Forcepoint ONE SSE portal, navigate to .
-
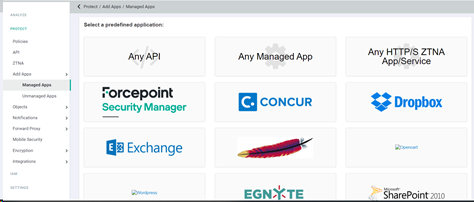
On the Managed Apps page, select the Forcepoint Security Manager option.
The FSM page opens populating the Application Name, Current Application Logo, Current Application Icon, Service, and Port details.
Note: You can modify these fields, if required.
-
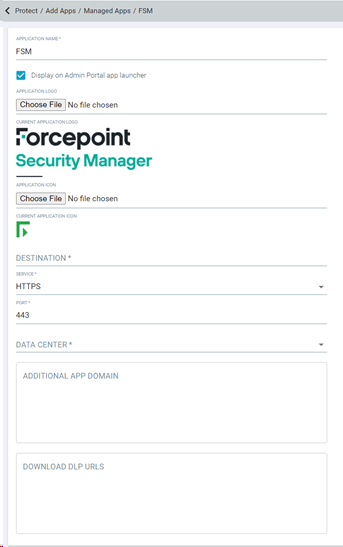
Enter the Application Name.
-
Select the Display on Admin Portal app Launcher to display the Application Name on Admin Portal app
Launcher.
-
To change the Application Logo, click the Choose File and navigate to the application logo from your machine and then click
Ok to upload it.
-
To change the Application Icon, click the Choose File and navigate to the application icon from your machine and then click
Ok to upload it.
-
Enter the internal hostname for your app. The hostname of app should also include domain name.
-
Select Server Type. For FSM, this field should be set to HTTPS.
-
Enter the Port that is accessed over. For FSM, this field should be set to 9443.
-
Select the Data Center name that is applicable for FSM. This is a name that is used in logs.
-
Enter any other additional domains associated with the app to ensure full functionality when a user is being proxied to the app.
-
Once you are done with the changes, click Save.
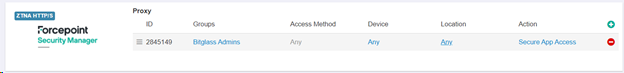
A default ZTNA app gets created in with the Groups set to Bitglass Admins. You can apply contextual access controls and inline DLP policies just like
any other cloud app (notice it will indicate the app as being ZTNA in the top left of the app logo). You can learn about policy configuration on the Configuring
contextual access control and Configuring proxy policy actions.