Private applications policy
Added 19-Nov-2020 The Policy menu has been updated with the Private applications policy type. Private application policy rules are used to identify and authenticate the users that are permitted to access your private applications, and apply block, continue, or bypass actions. Traffic decryption and threat inspection are deployed to inspect traffic payloads and identify potential threat signatures in private application traffic.
Private application policy rules are applied to all incoming requests for your internal resources from remote users in your account. Private application traffic that is routed through a Private Access service edge for policy enforcement is checked against your policy rules for a match.
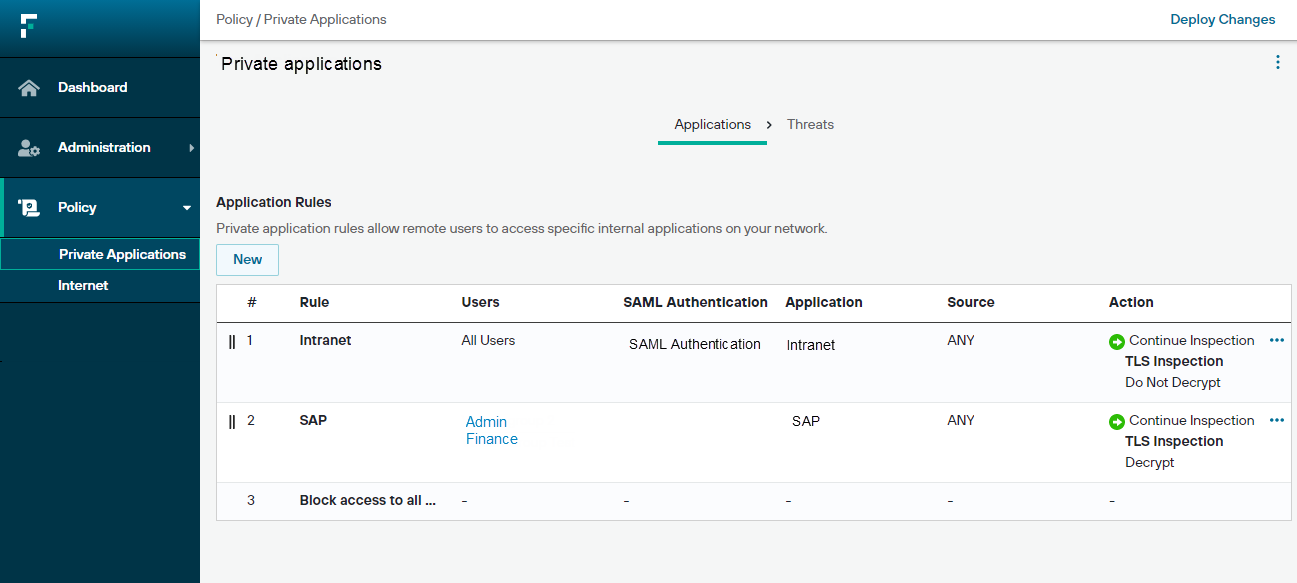
Policy rules are checked in priority order, and a default Block access rule blocks all traffic that is not explicitly matched by another rule. You can apply Source IP address lists and Countries to filter incoming traffic based on IP address or geographic location.
Policy rules can be applied to users or user groups. Users are provisioned to the service using a SCIM-compliant identity provider, and identified to the service seamlessly using the endpoint client. SAML-based authentication for private application traffic will be added in a future update.