Audit log
Audit logs are generated when any of the following happen: create, edit, or delete of a new user, password change, generation of master, endpoint, or bypass release code, deleting an endpoint, exporting data, changes to over-the-air (OTA) update configurations, changes to device control policy etc.
An audit trail is a security-relevant chronological set of records that provide documentary evidence of the sequence of activities that have affected at any time a specific operation, procedure, or event done by the Forcepoint Data Security Cloud | DLP cloud portal administrators, analysts, and helpdesk users.
Audit log records are stored for 6 months on the management portal.
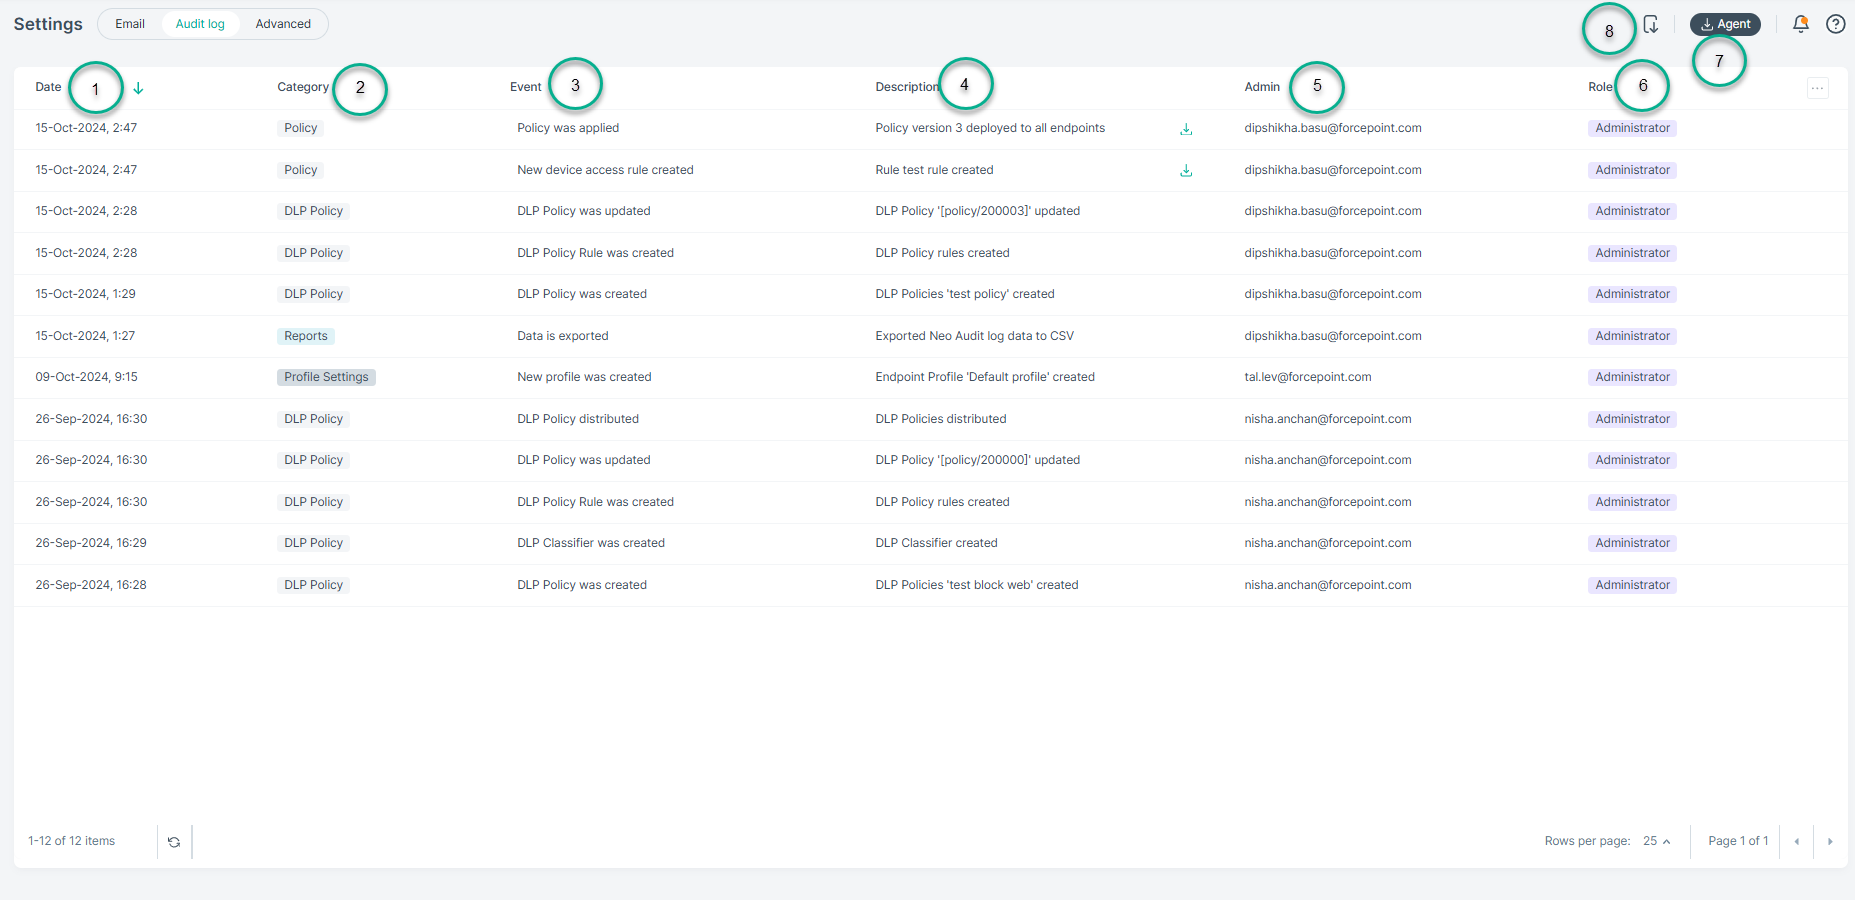
- 1
- Date: Specifies the date the event occurred.
- 2
- Category: Specifies the event category.
- 3
- Event: The event that caused the audit log generation.
- 4
- Description: Event detailed description.
- 5
- Admin: Cloud portal user responsible for the action.
- 6
- Role: The role assigned to the user.
- 7
- Download Agent: Allows for downloading the latest agent version and and navigate to the agent download page if the administrator wishes to install a previous version of the agent.
- 8
- Export to CSV: Allows for exporting the audit log data to a CSV file.