File fingerprint
Classify unstructured data by fingerprinting a known file or directory so a policy can recognize that data, or the files themselves, wherever they appear.
Overview
The File fingerprint view lets administrators classify unstructured data by fingerprinting a known file or directory, rather than matching against a pattern. An administrator points the classifier at a single file, or a directory containing many files, and Forcepoint Data Security Cloud | DLP generates a fingerprint of that content. A policy can then recognize that data — or the files themselves — wherever it appears.
To access this view:
- Navigate to Policy >
Data protection, and click Policy Elements.
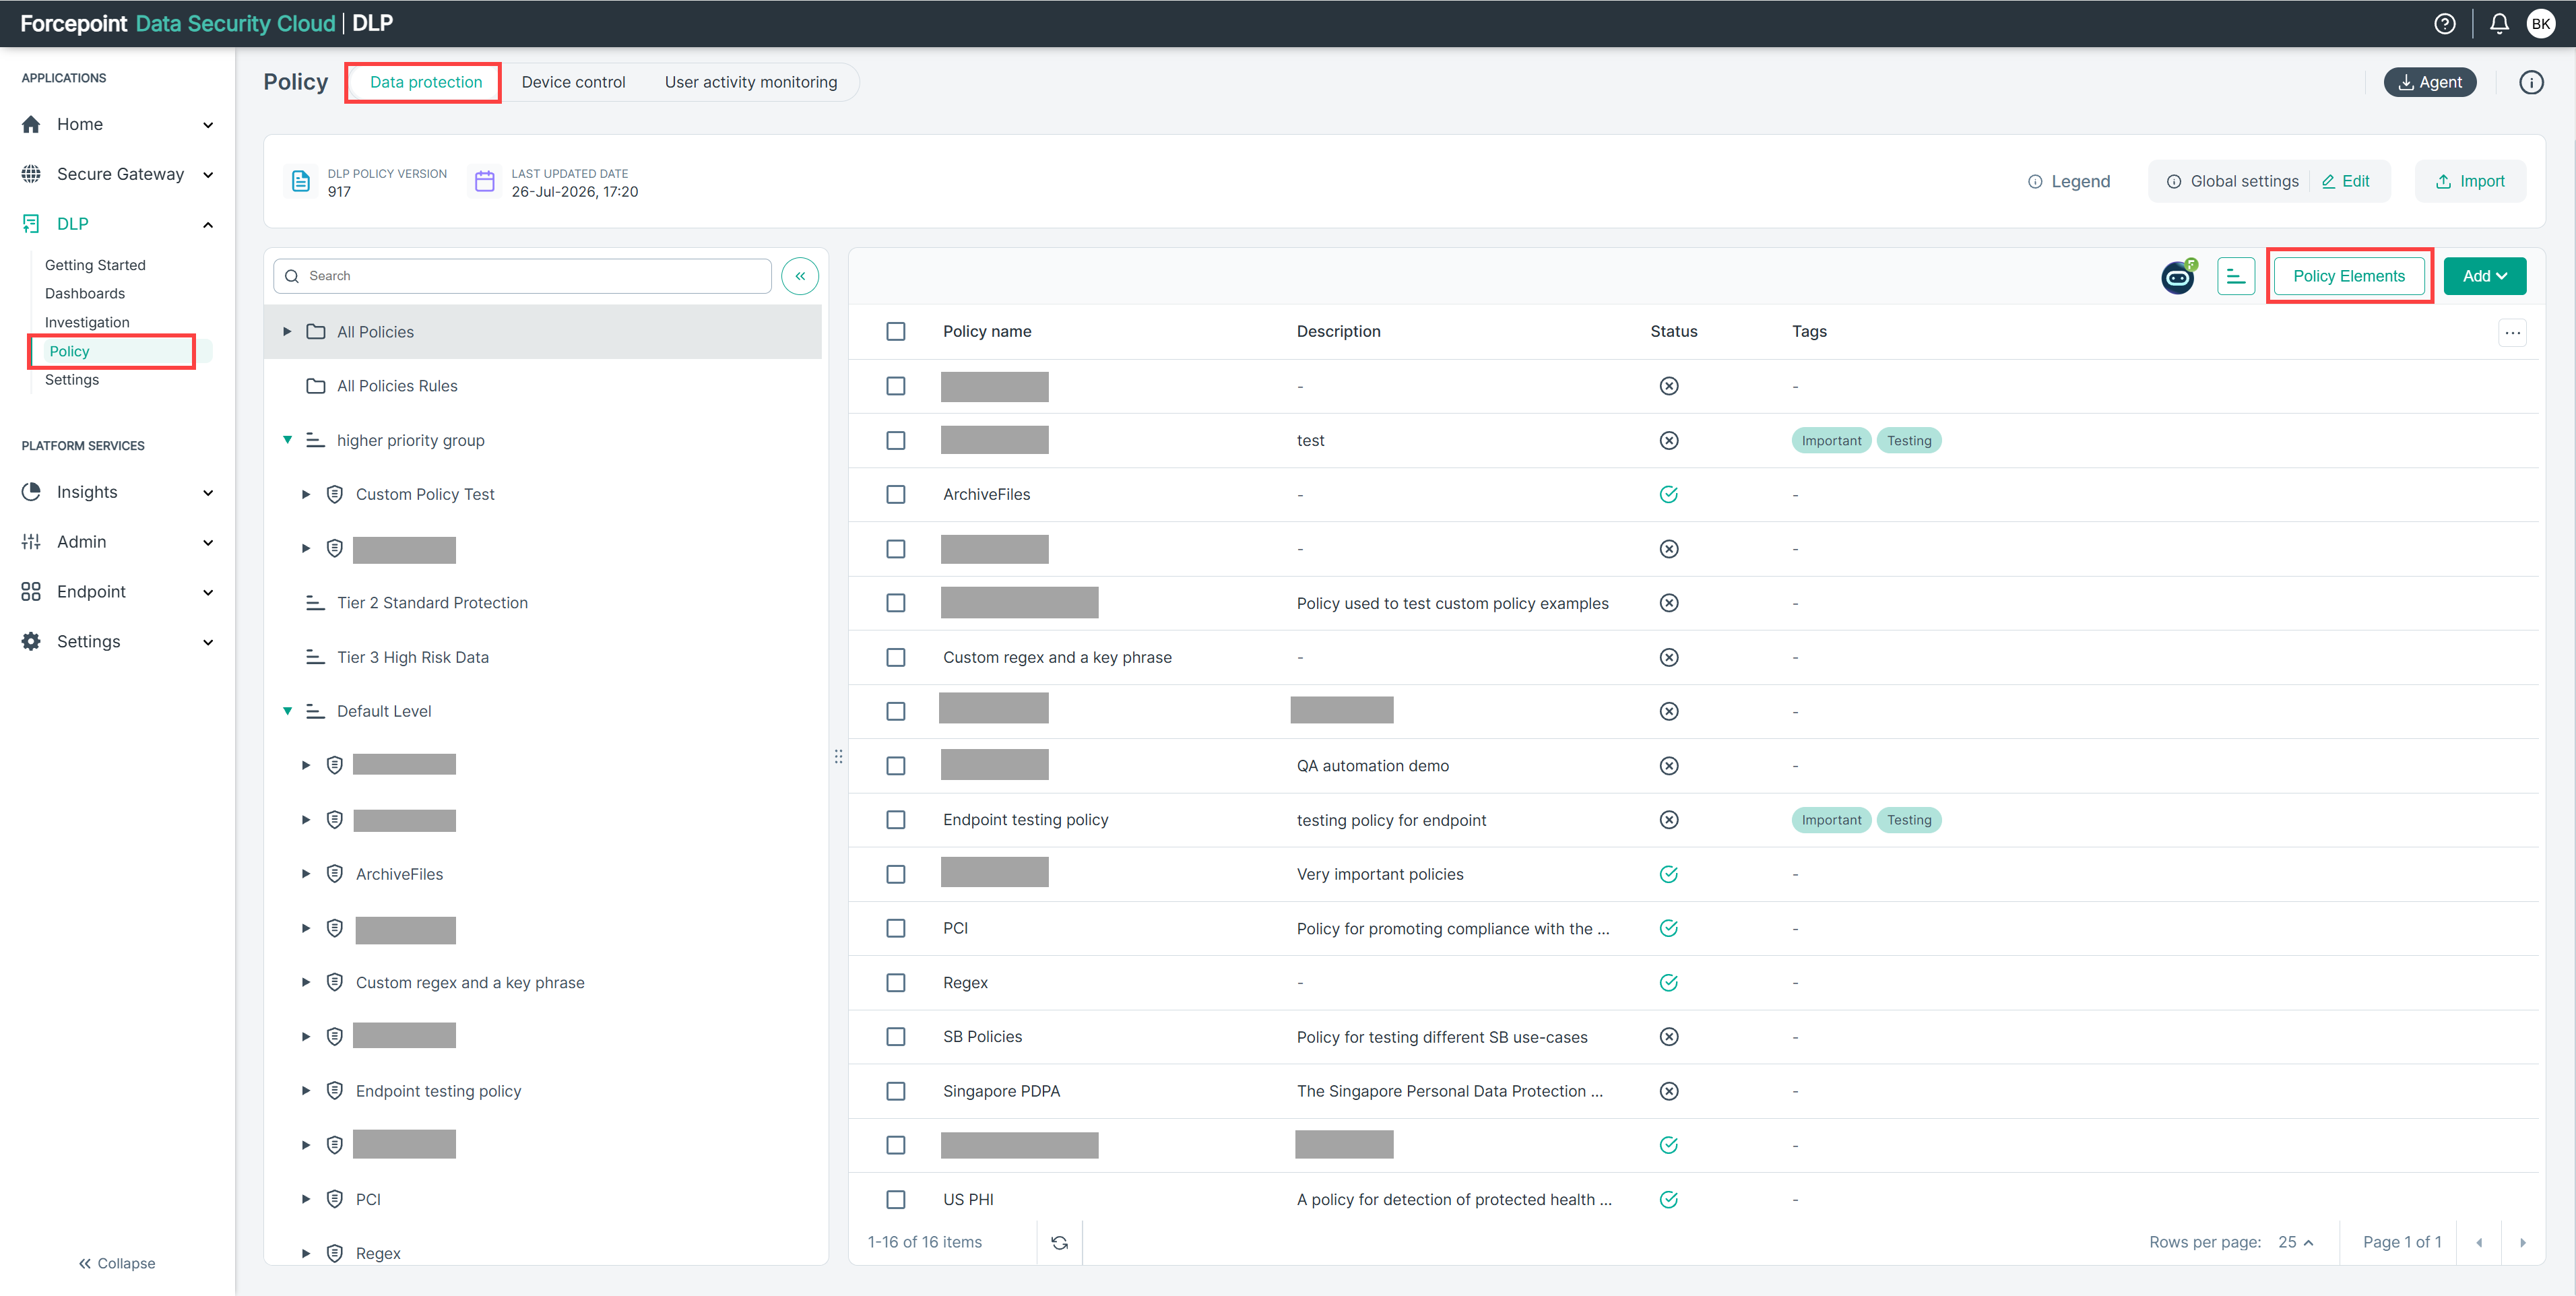
- The Policy Elements panel opens.
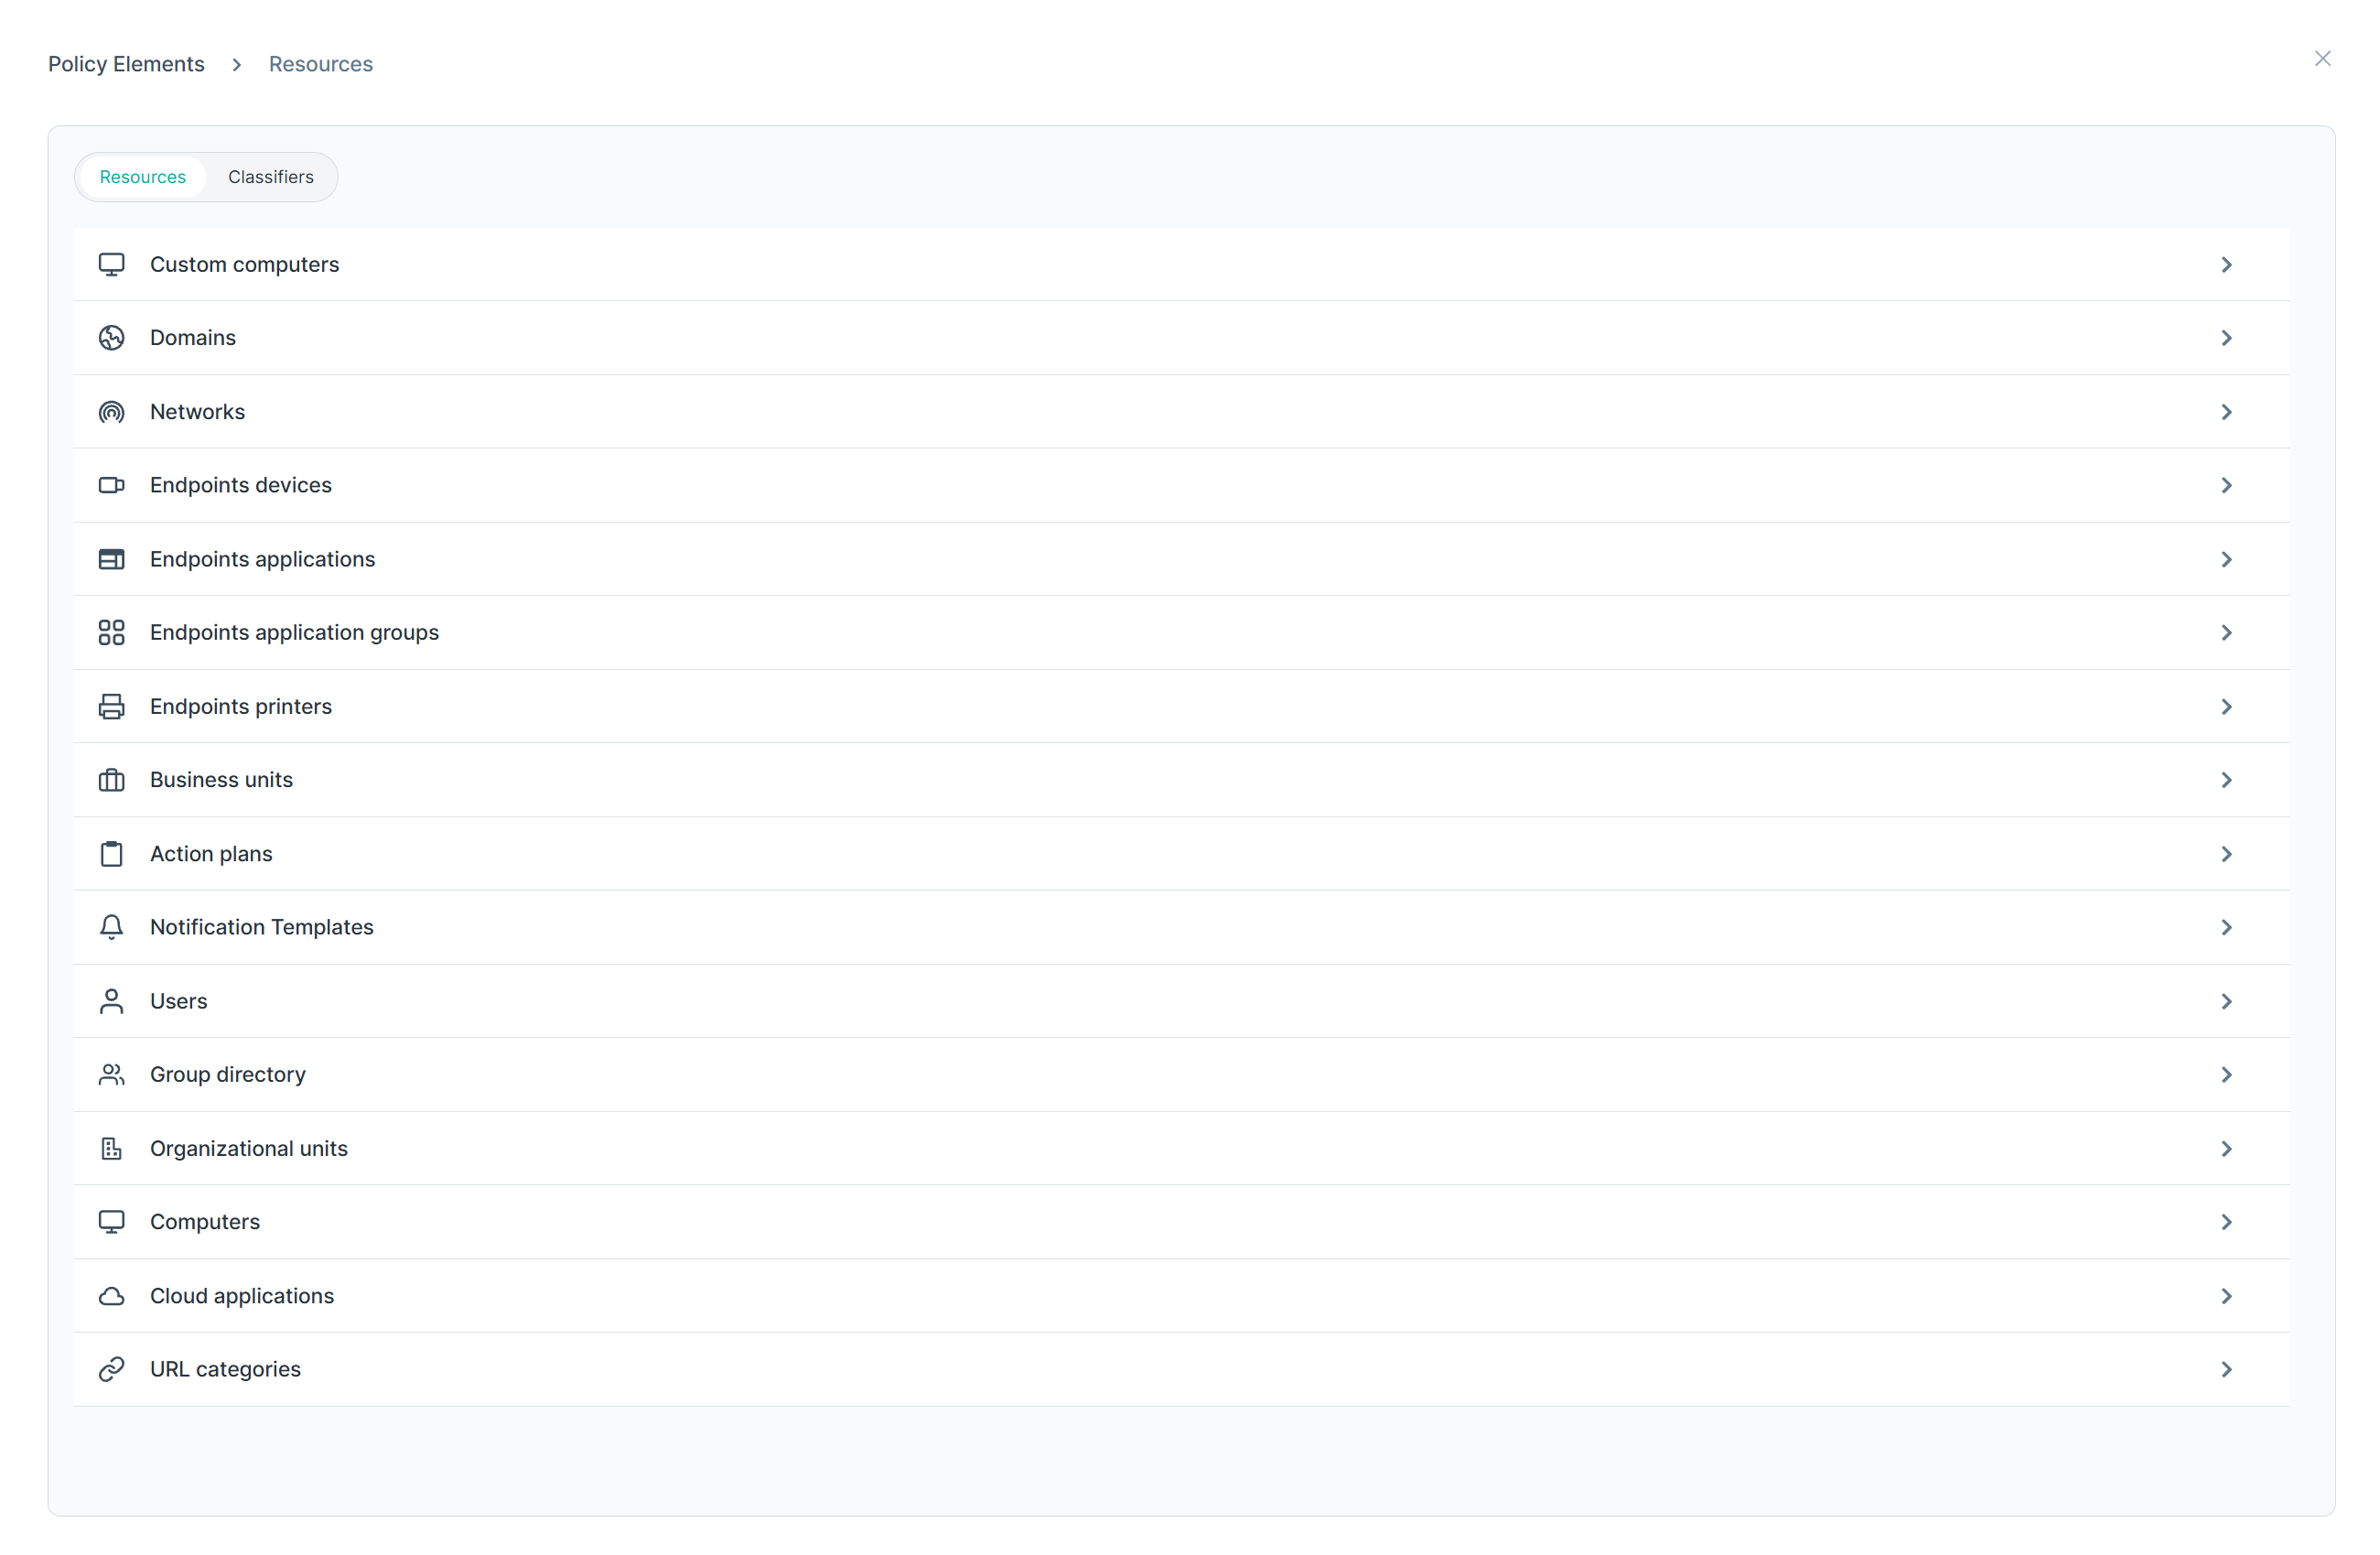
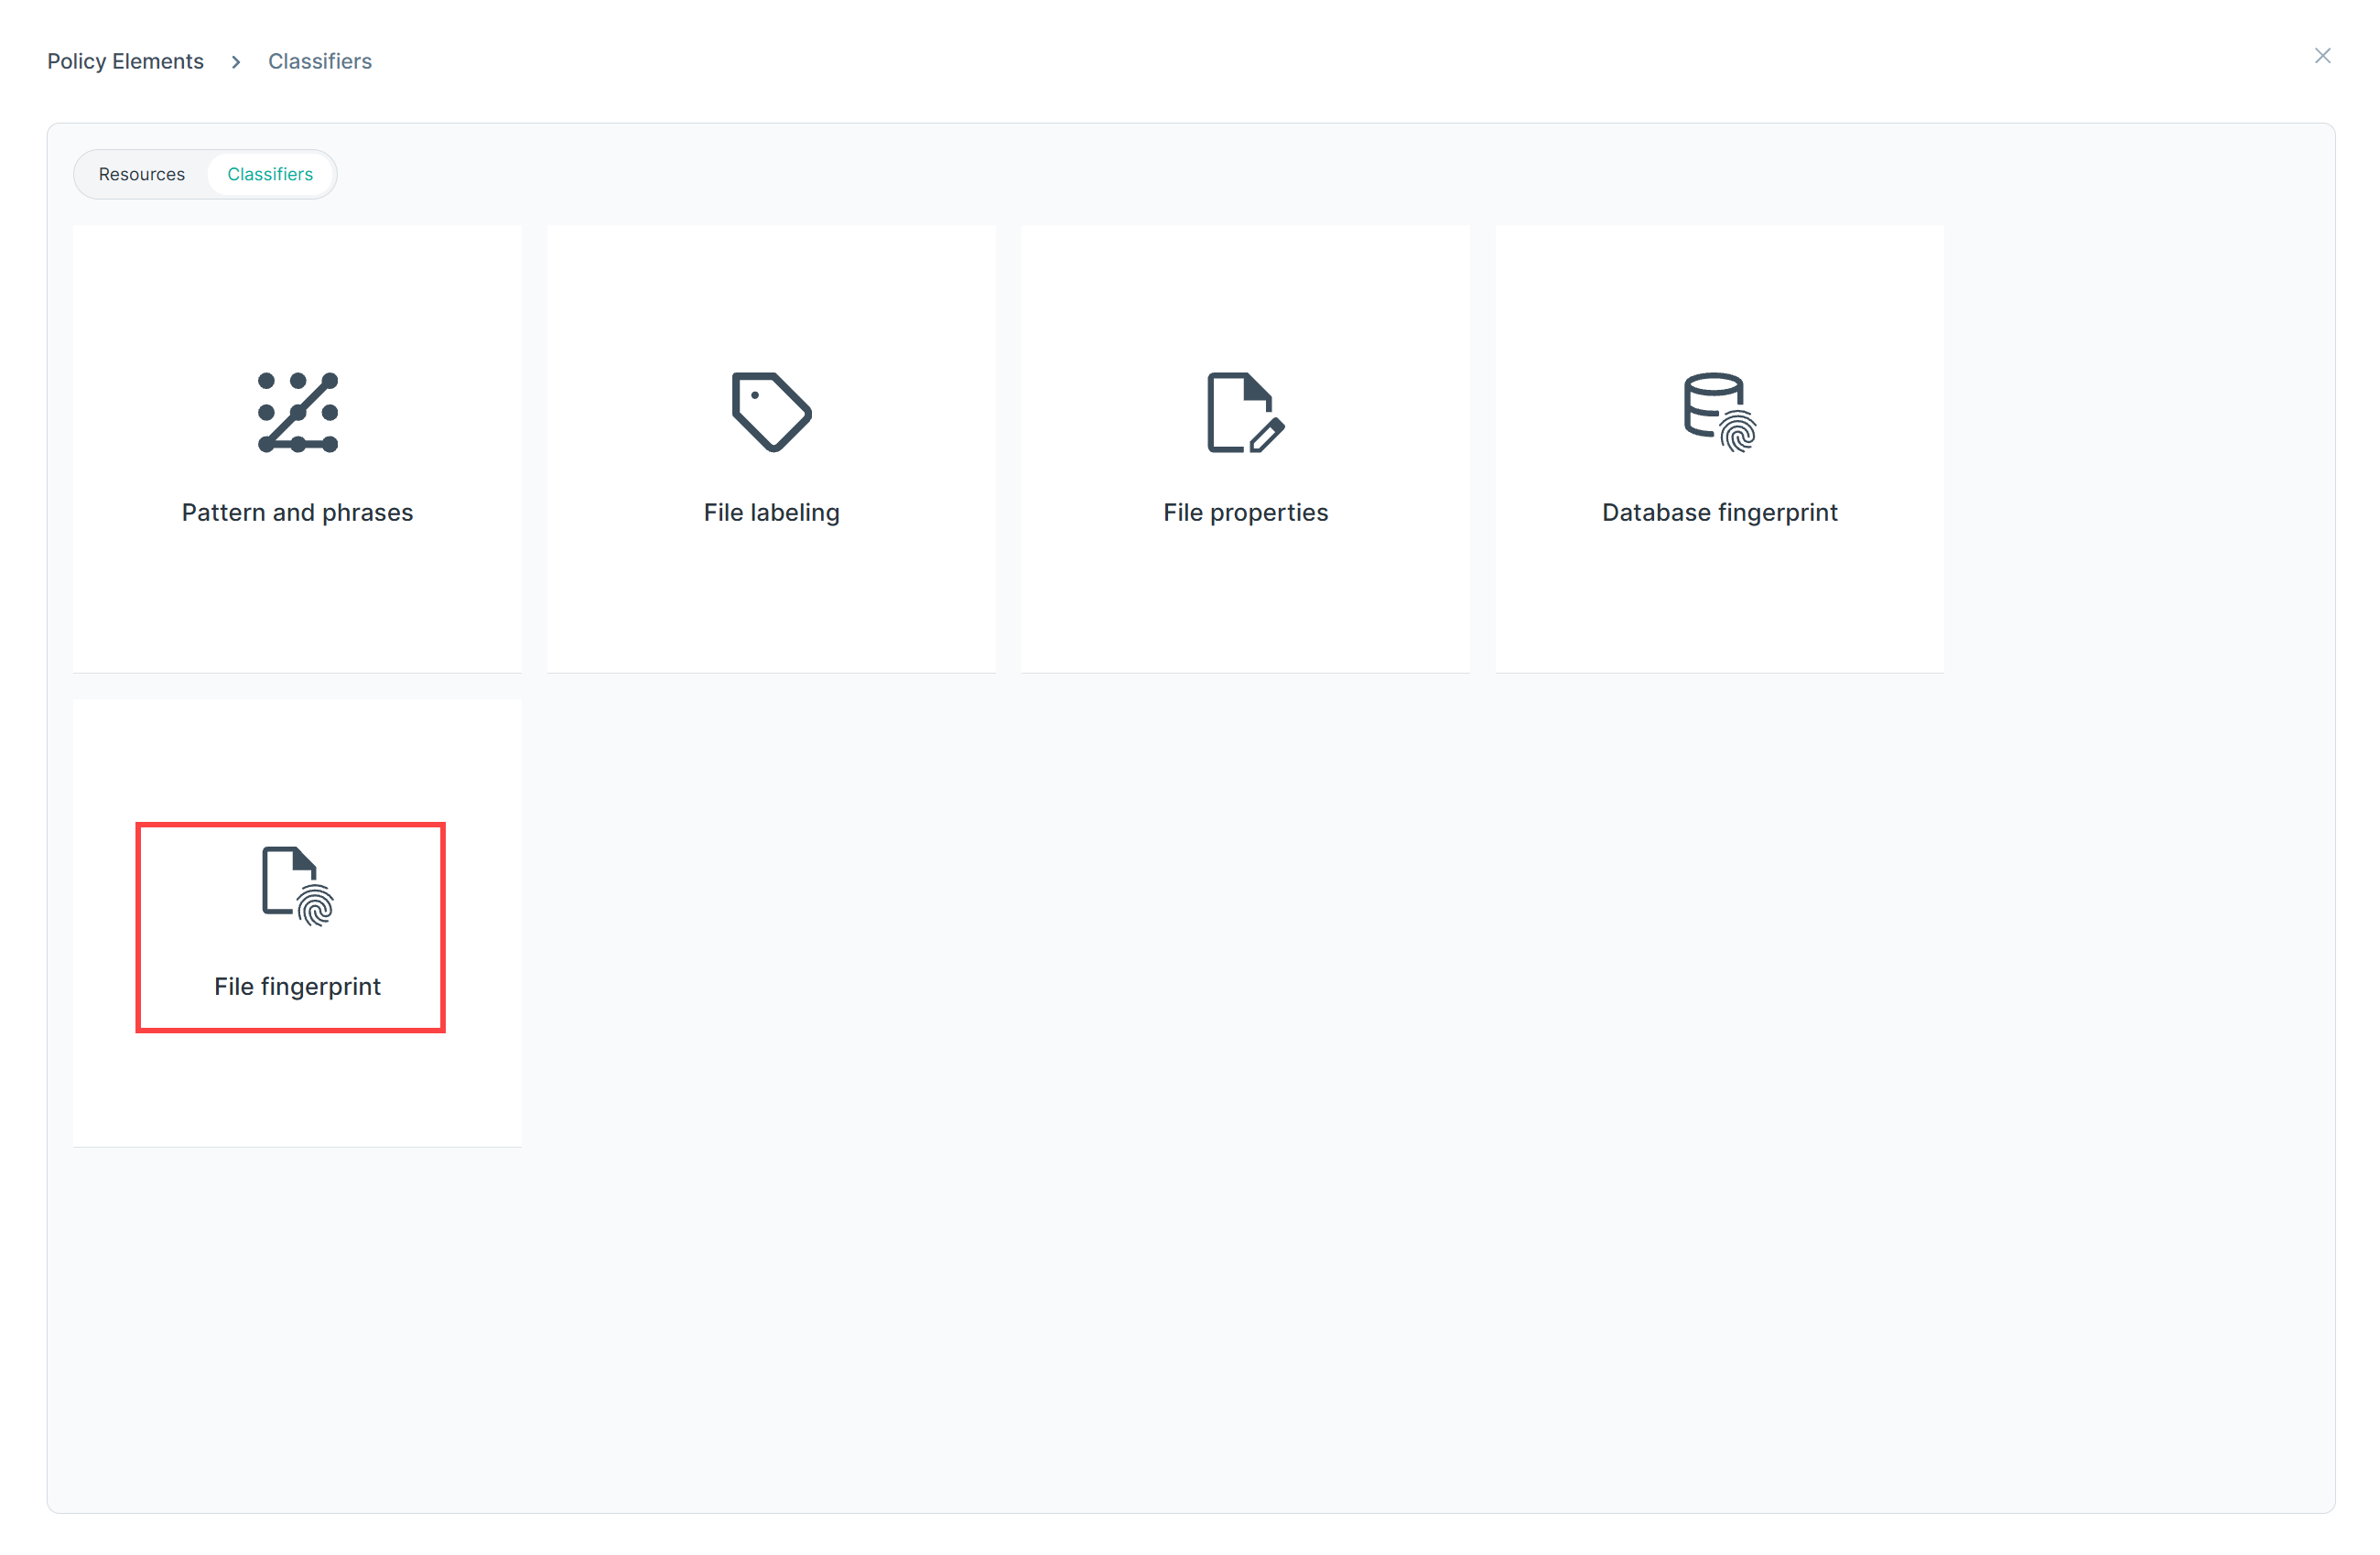
- In the Policy Elements panel, select the Classifiers tab, then click File fingerprint.
- The File fingerprint view lists existing classifier definitions, and lets administrators browse definitions or import them from a file.
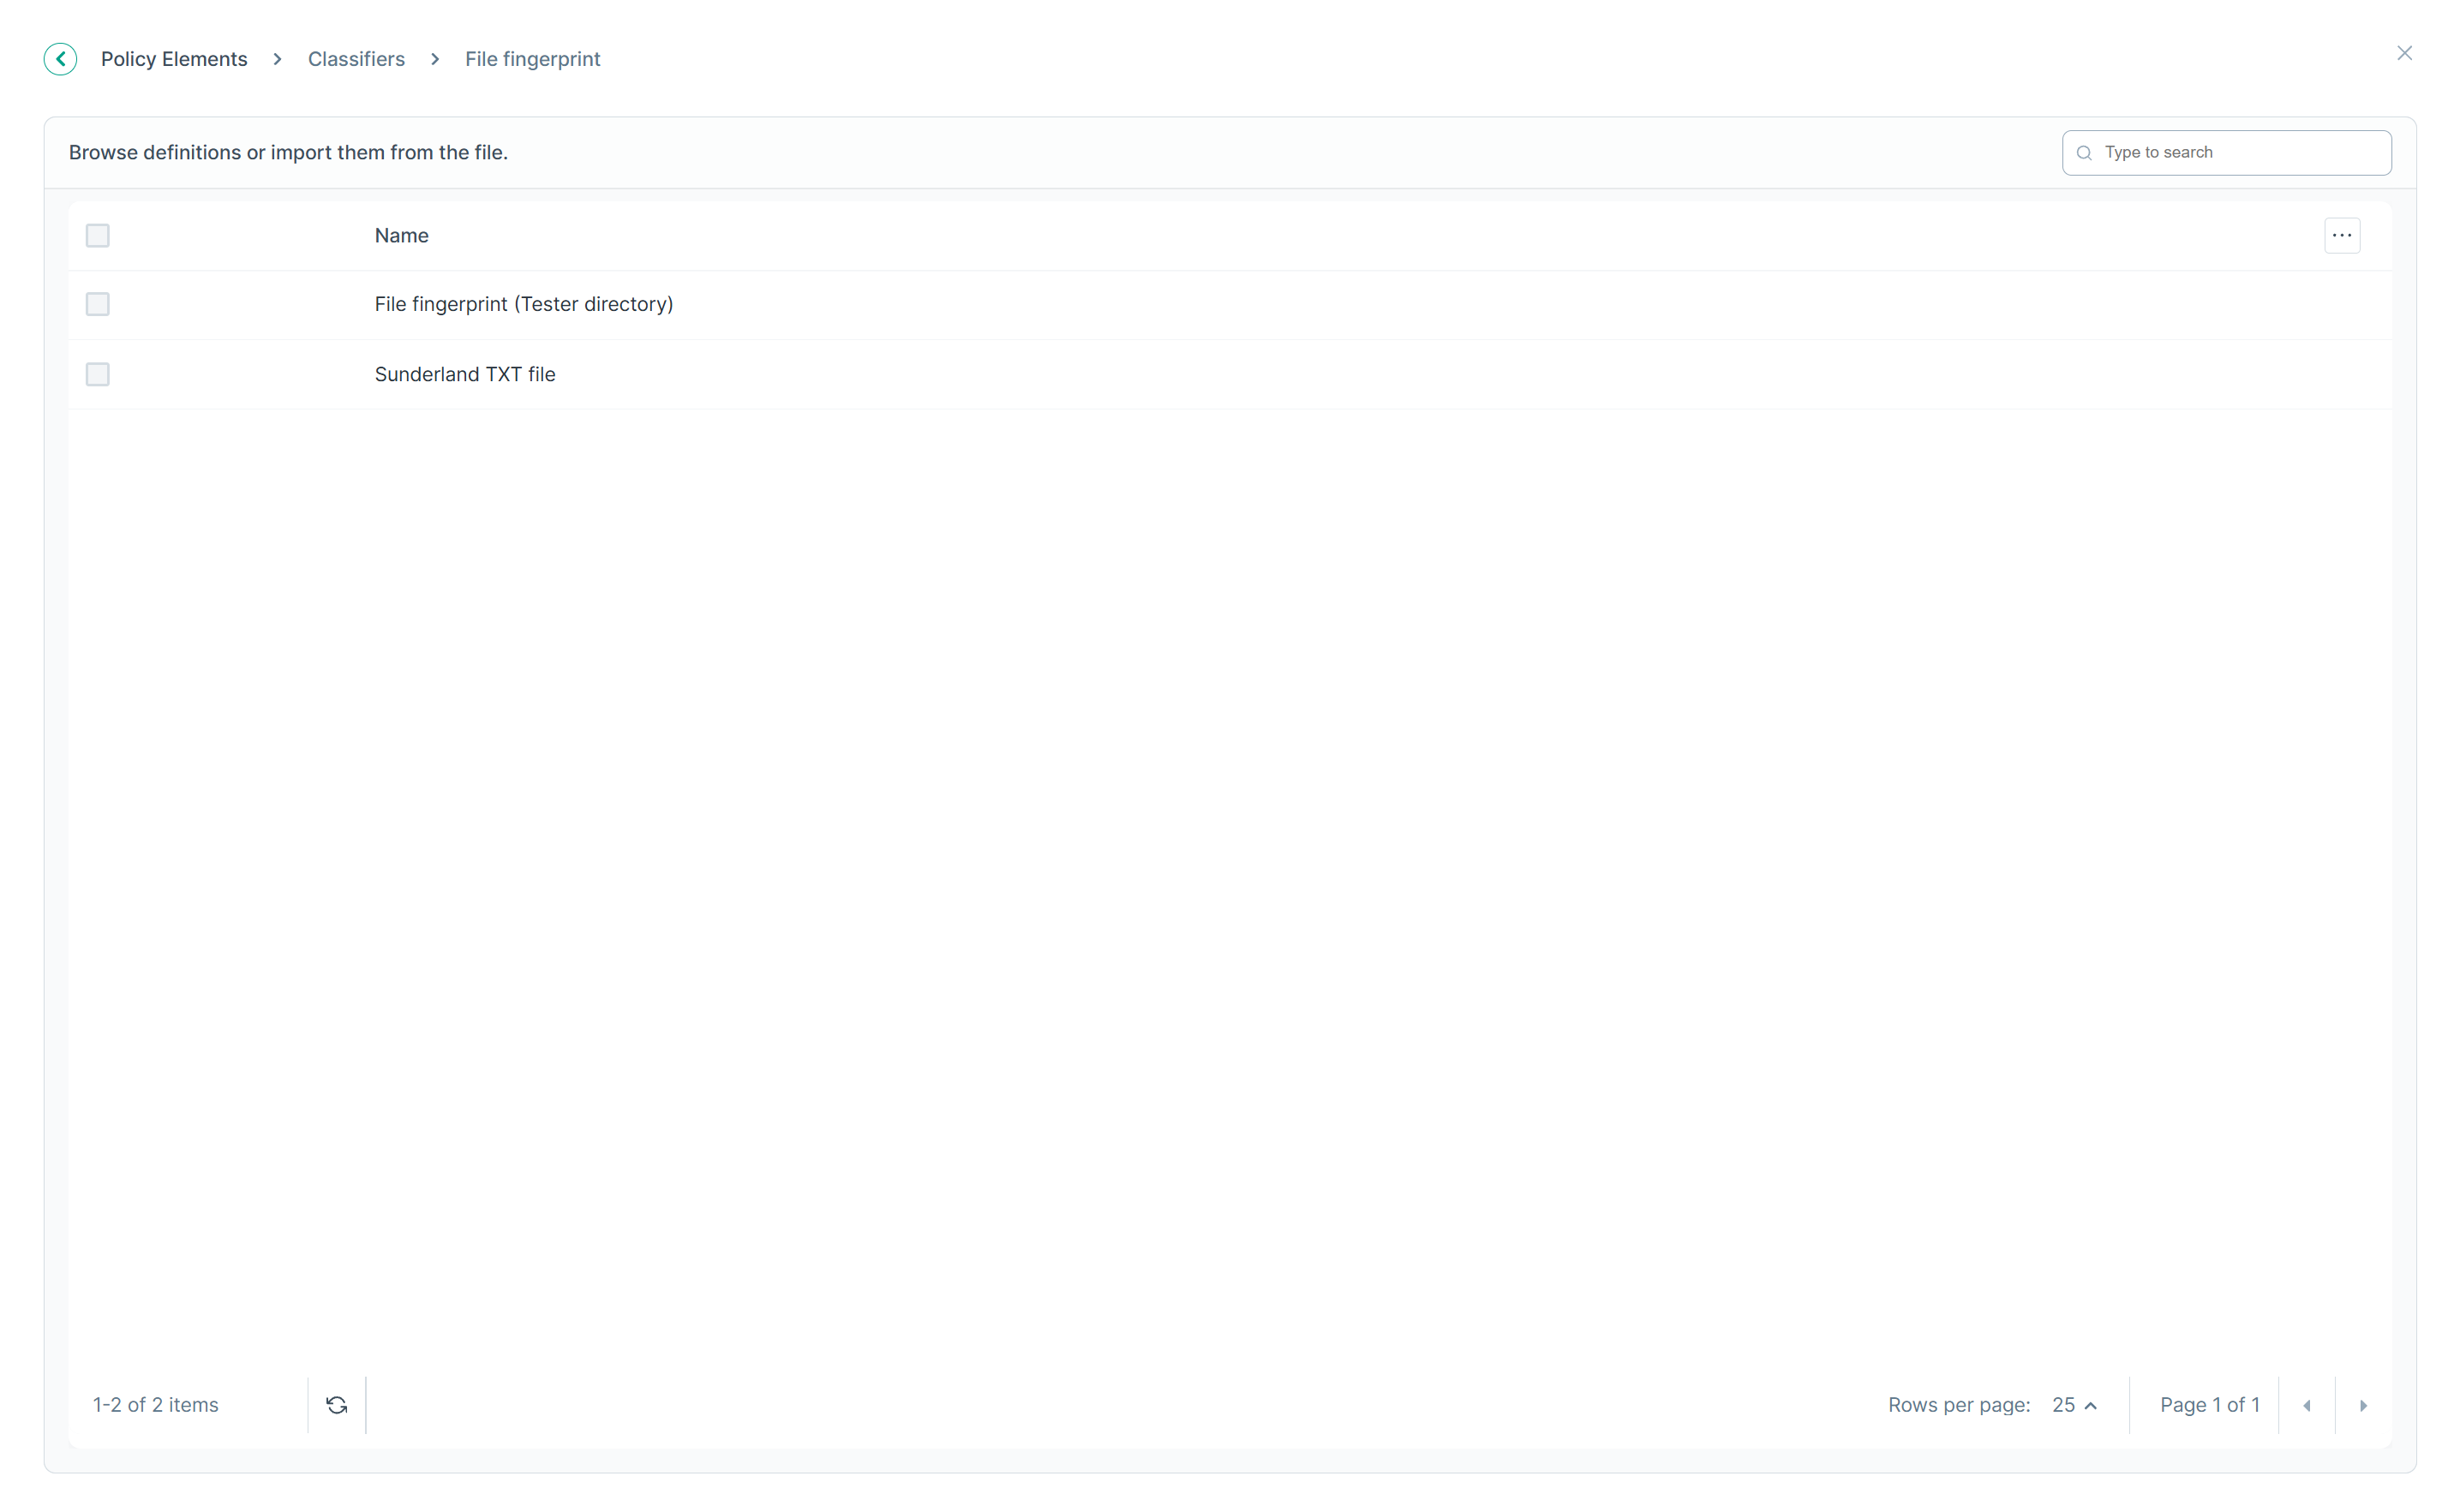
Column Description Name The name given to the file fingerprint classifier.
On-premises DLP and cloud DLP synchronization
Like Database fingerprint, File fingerprint classifiers are synchronized between the on-premises DLP and cloud DLP:
- On-premises DLP — where the fingerprint classifier can originally be created (e.g., pointing at a file or directory).
- Cloud DLP — a copy of the classifier is automatically synchronized from the on-premises DLP, where it appears under the same name and is available for use in cloud policies.Note: For details on creating and configuring a file fingerprint classifier on the on-premises DLP, see File fingerprinting in the on-premises DLP Administrator Help.
Using a File fingerprint classifier in a policy
Once created, a File fingerprint classifier is used the same way as any other classifier:
- Navigate to Policy menu.
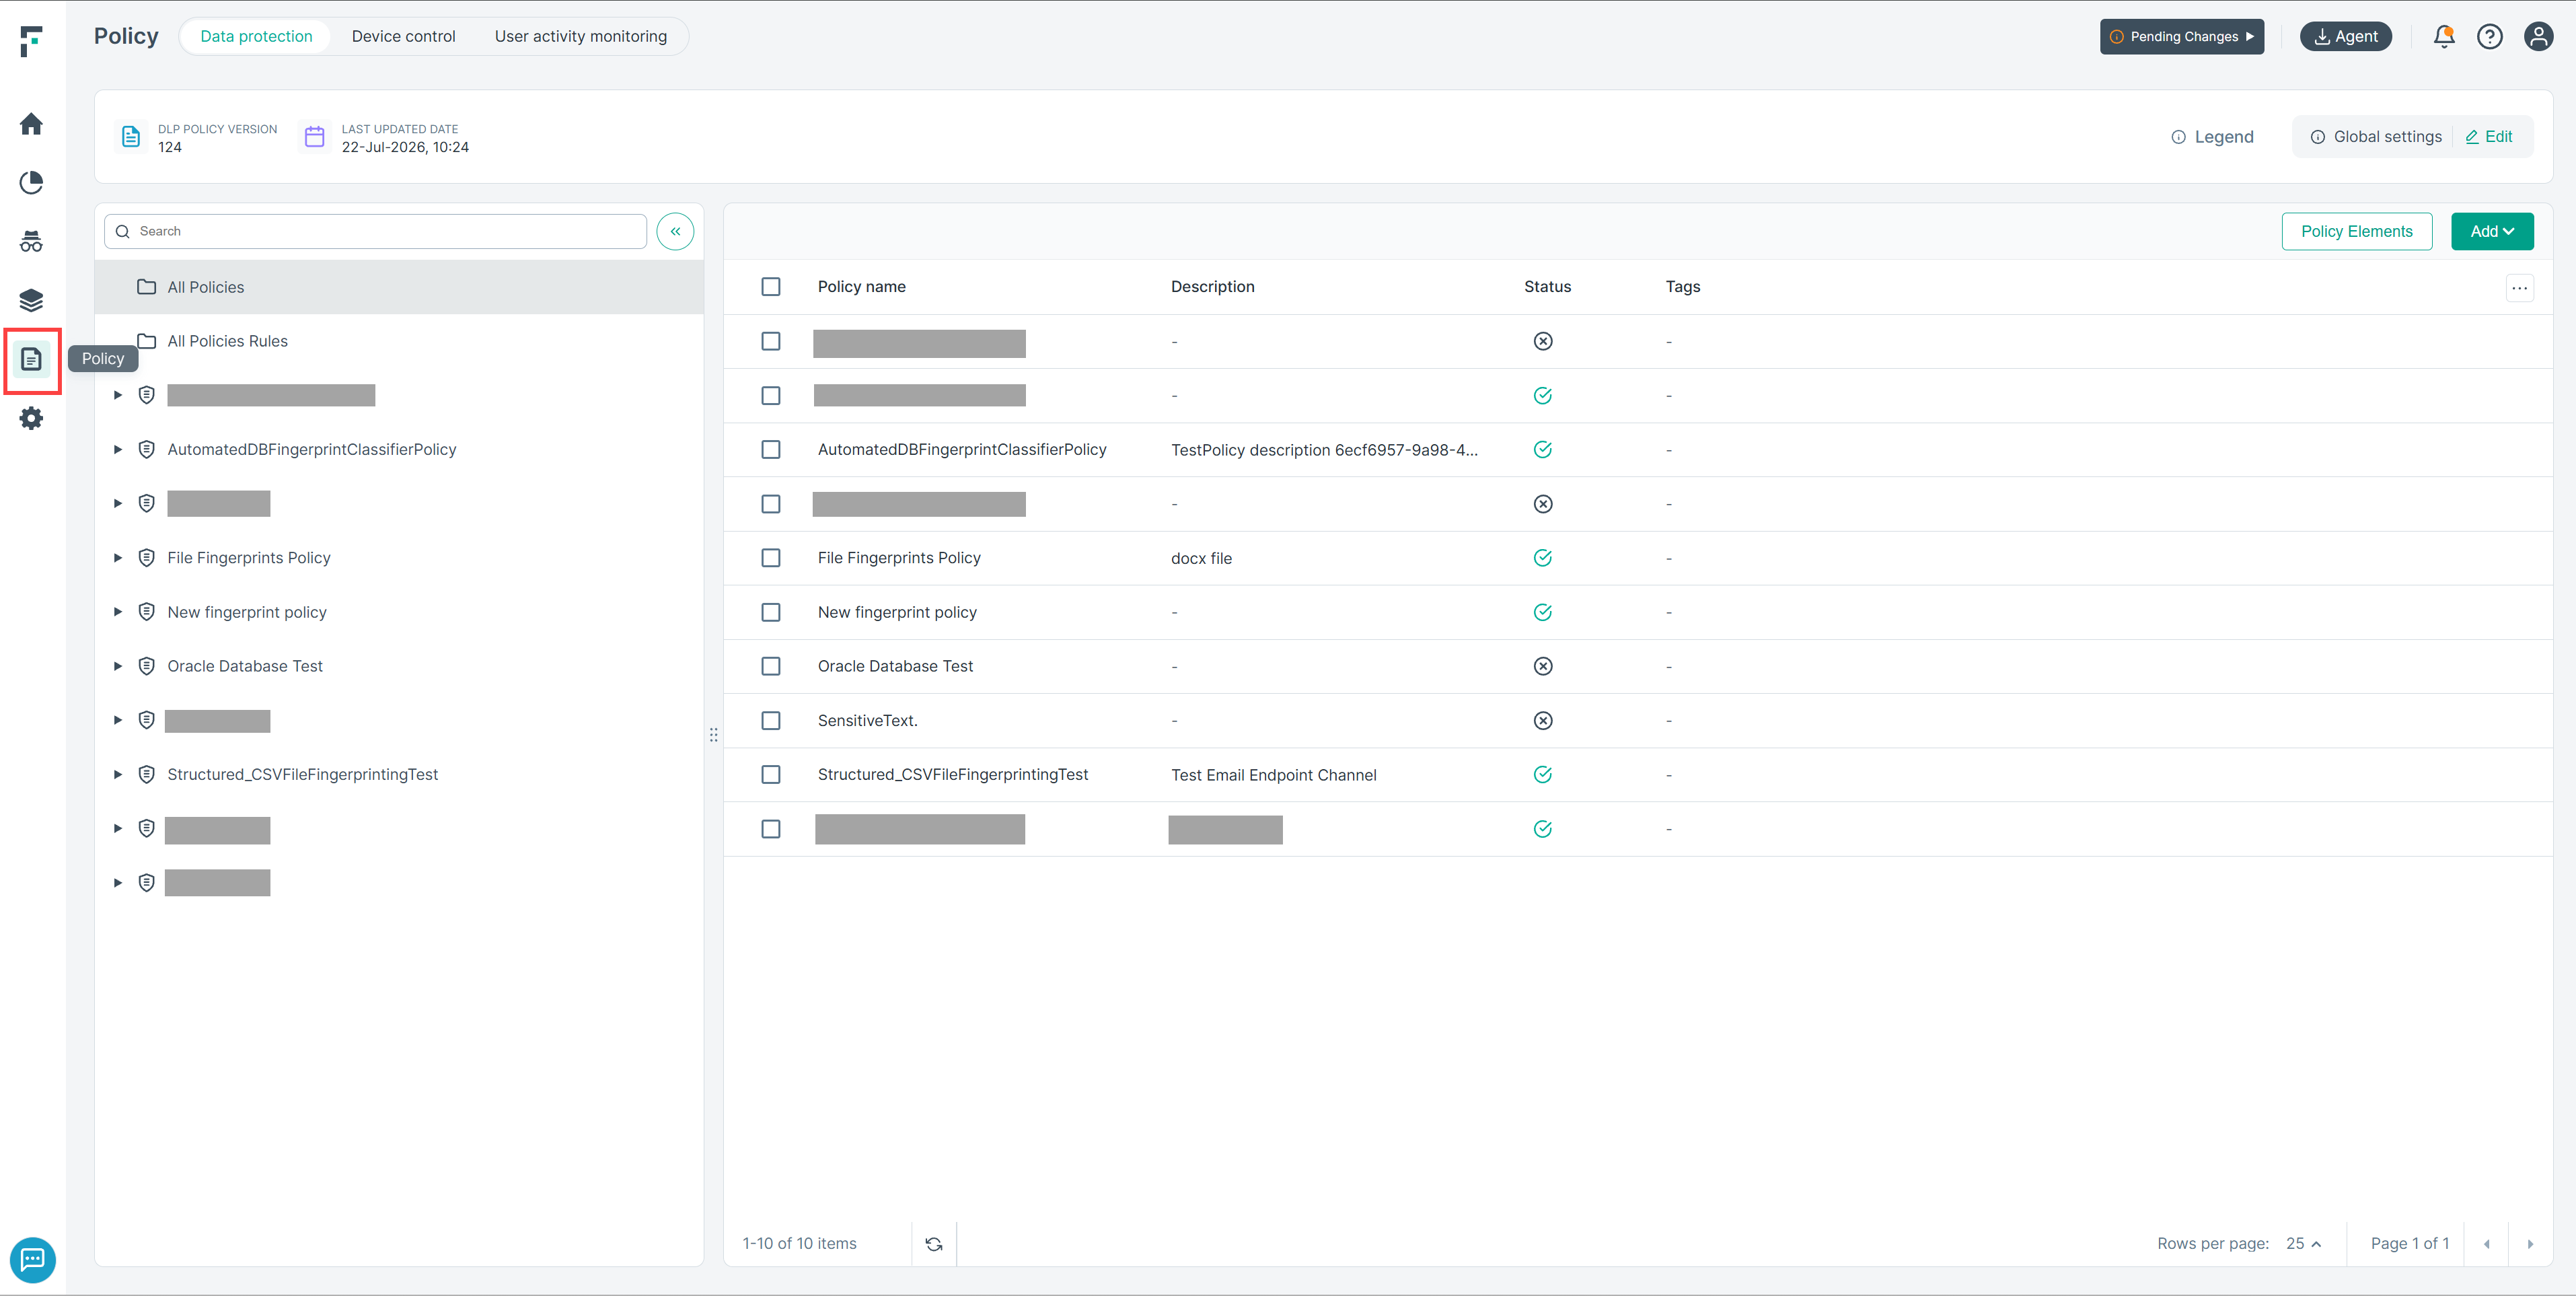
- Create or edit a policy rule.
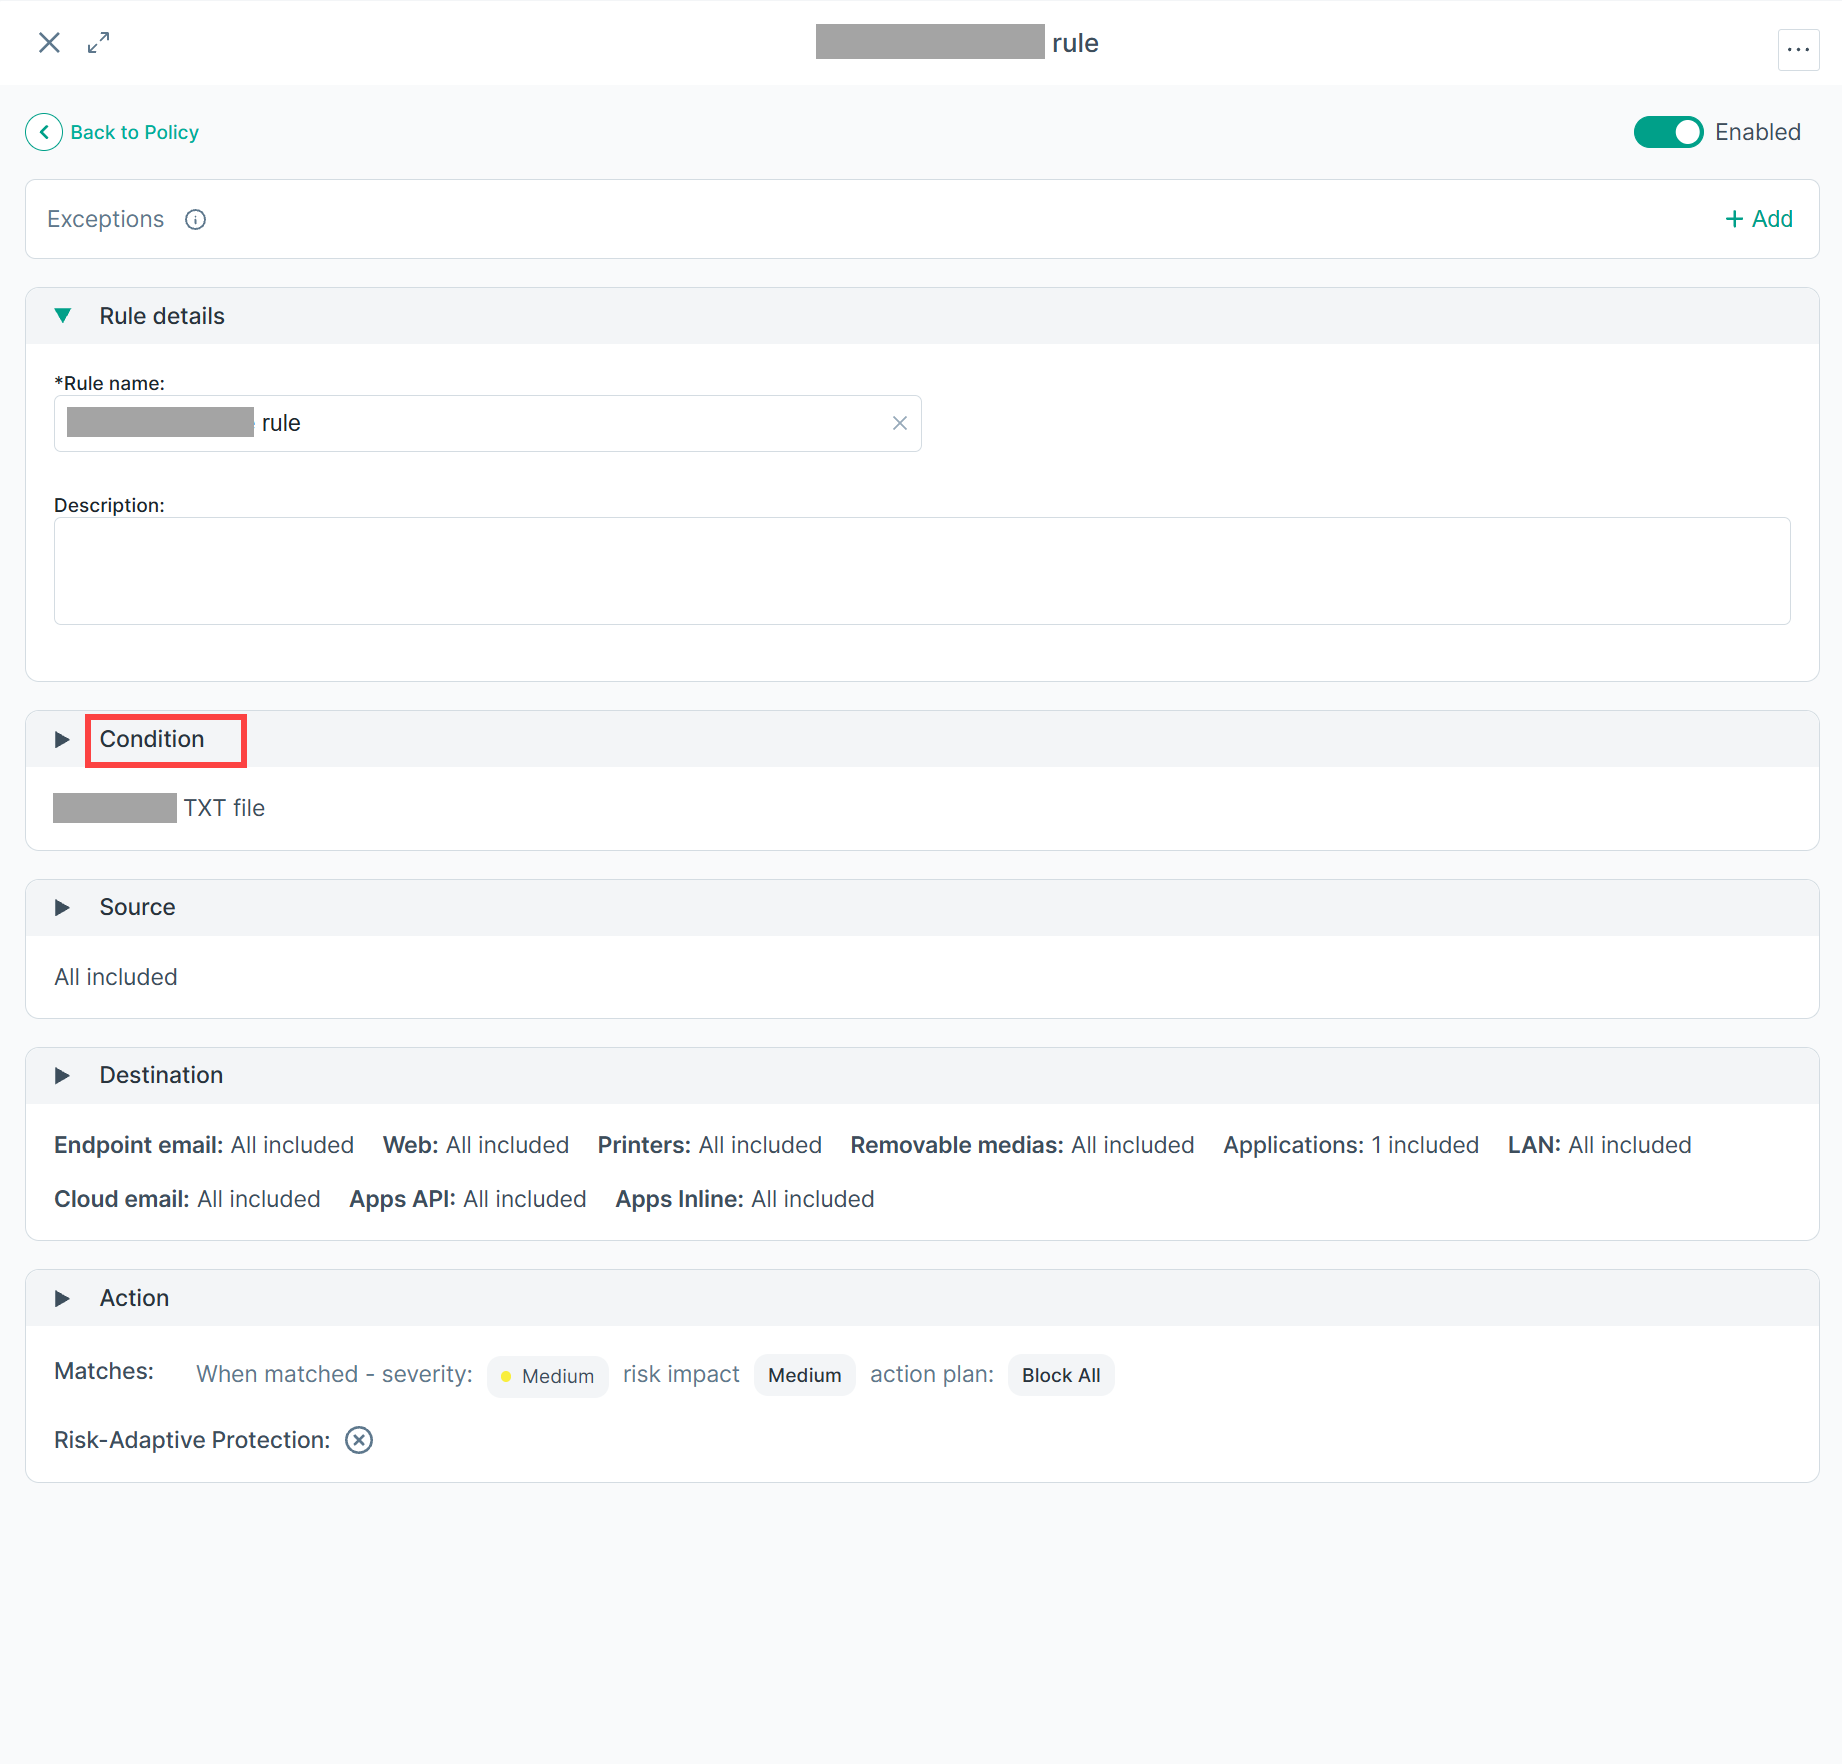
- Click Condition to expand and view the conditions.
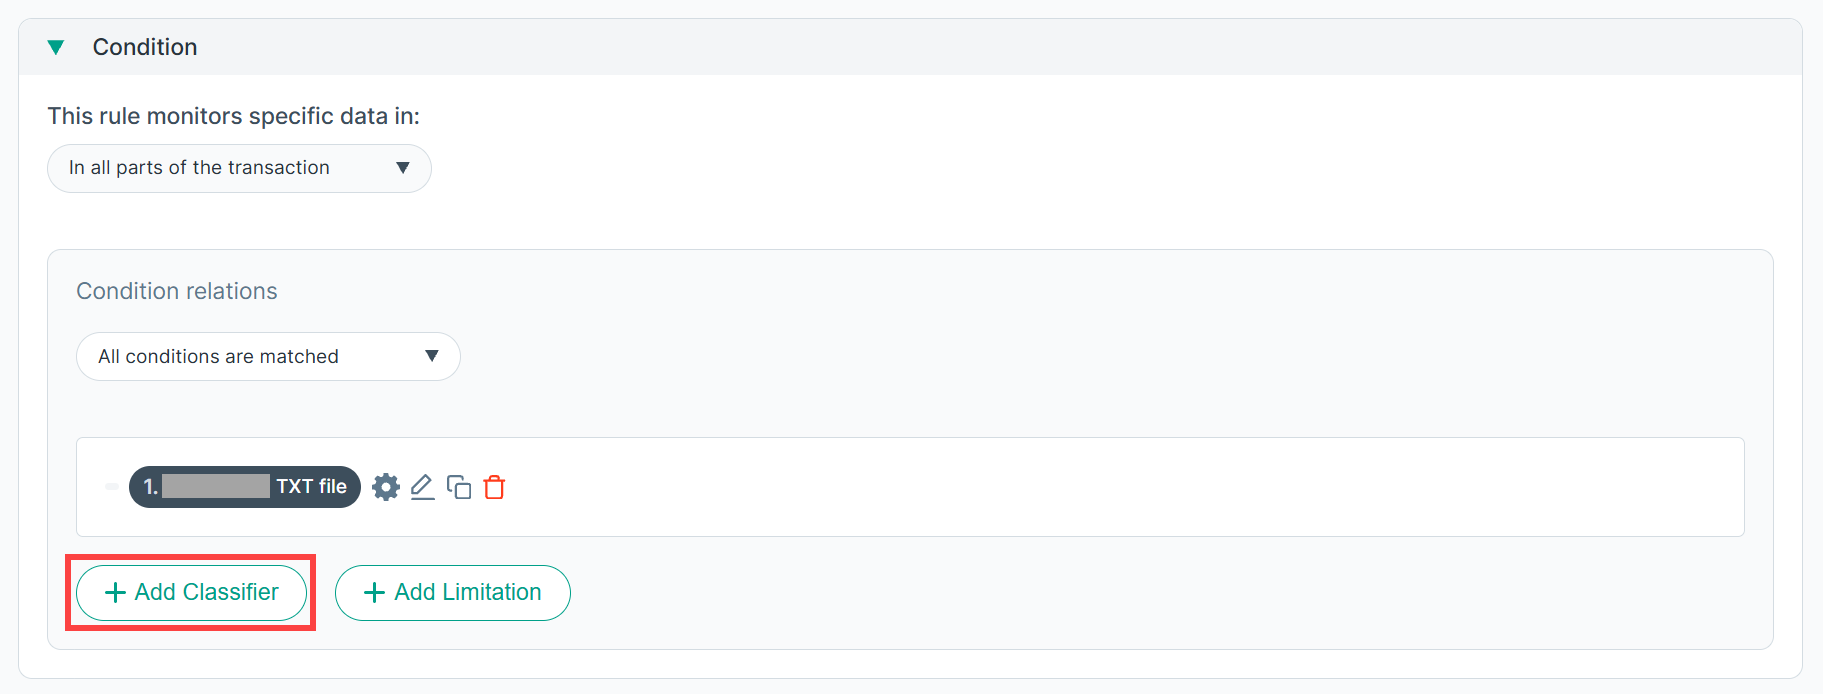
- Click Add Classifier.
- Filter by classifier type: File fingerprint.
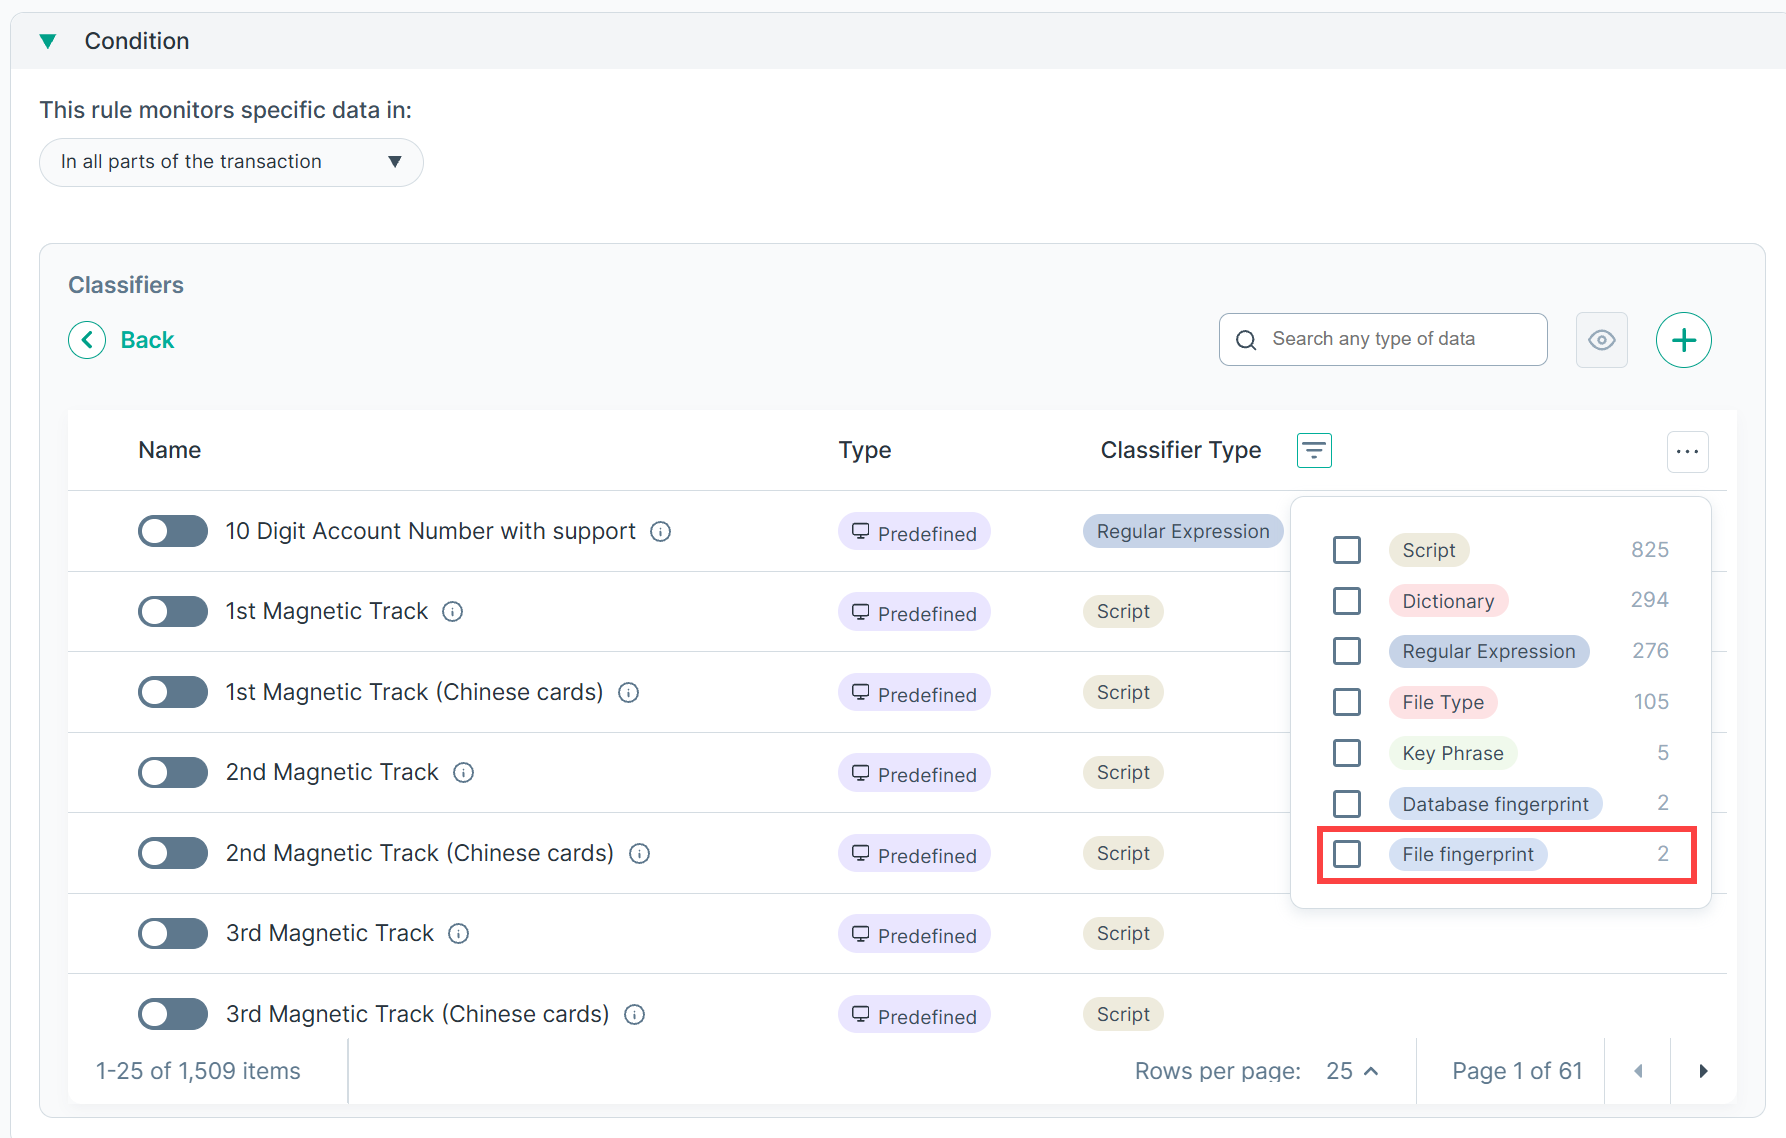
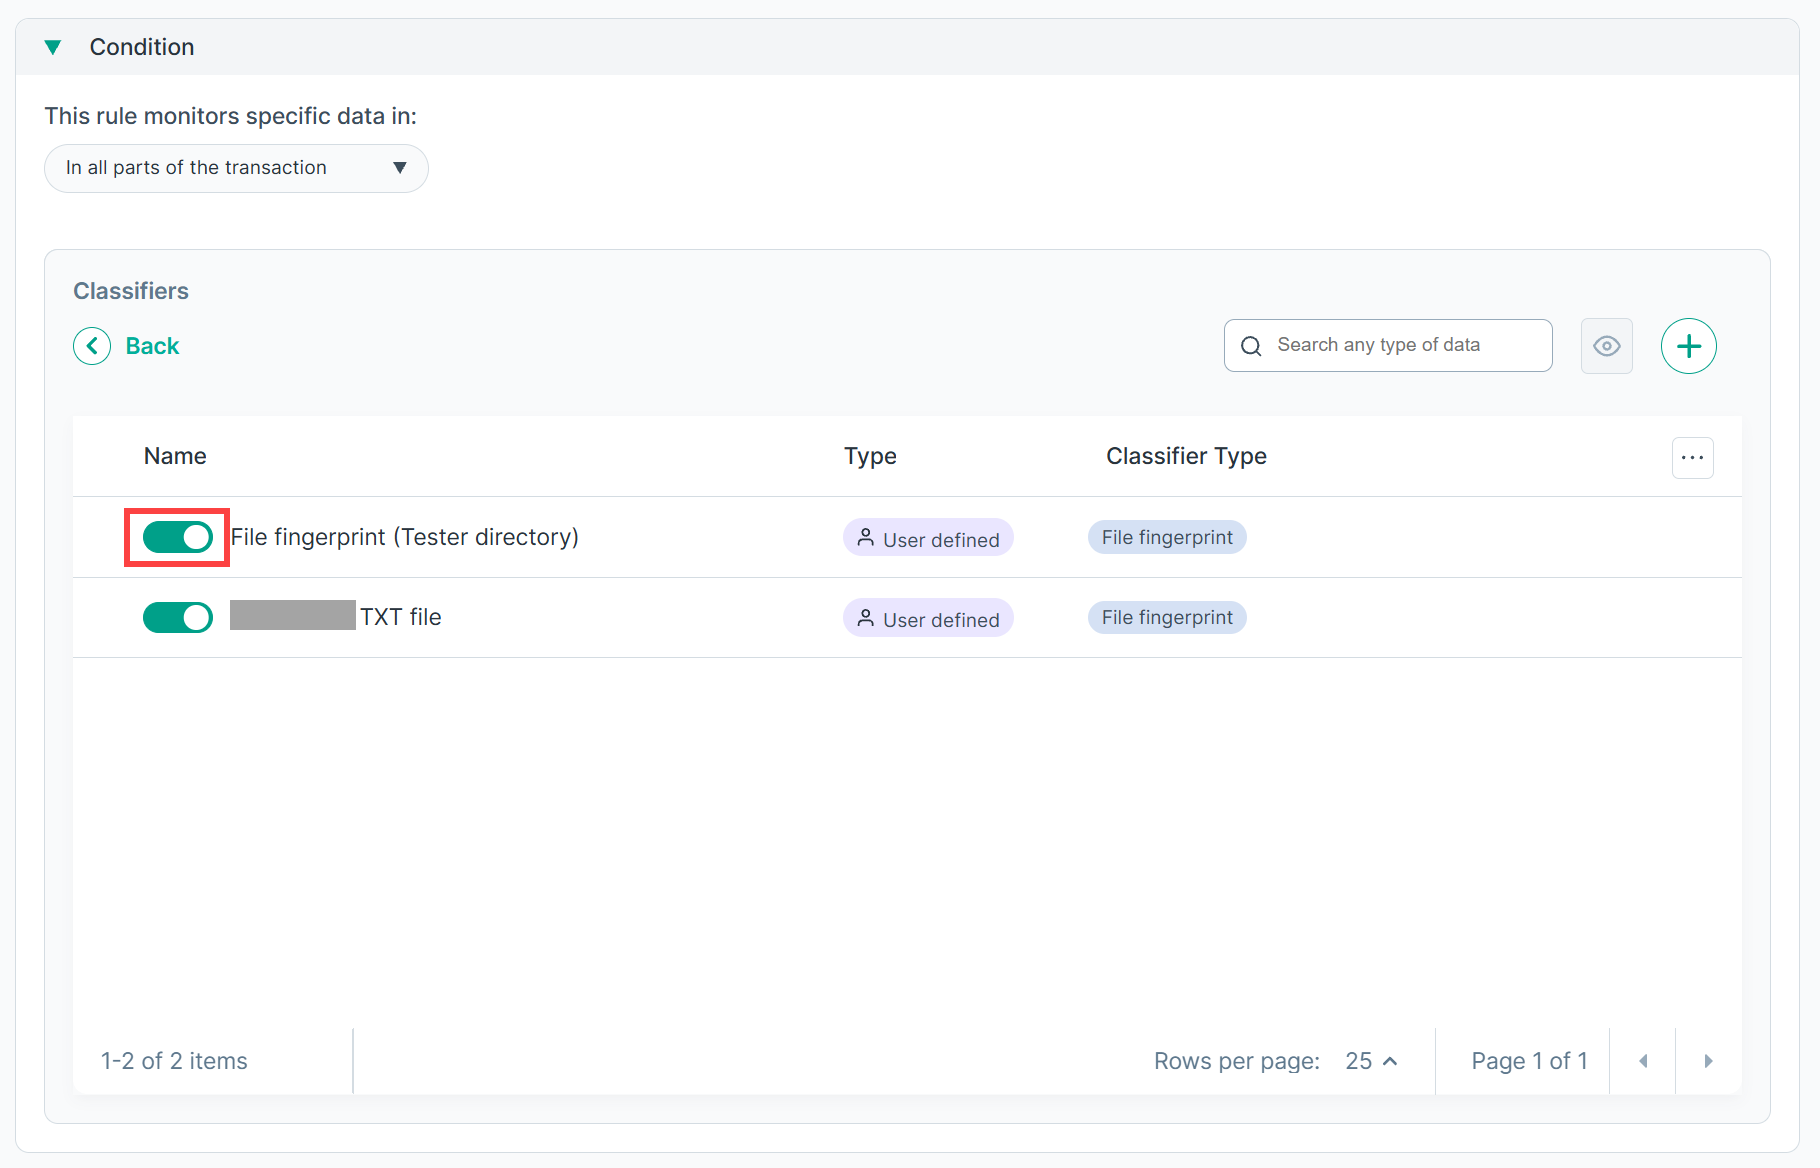
- Toggle on the specific File fingerprint classifier(s) to include.
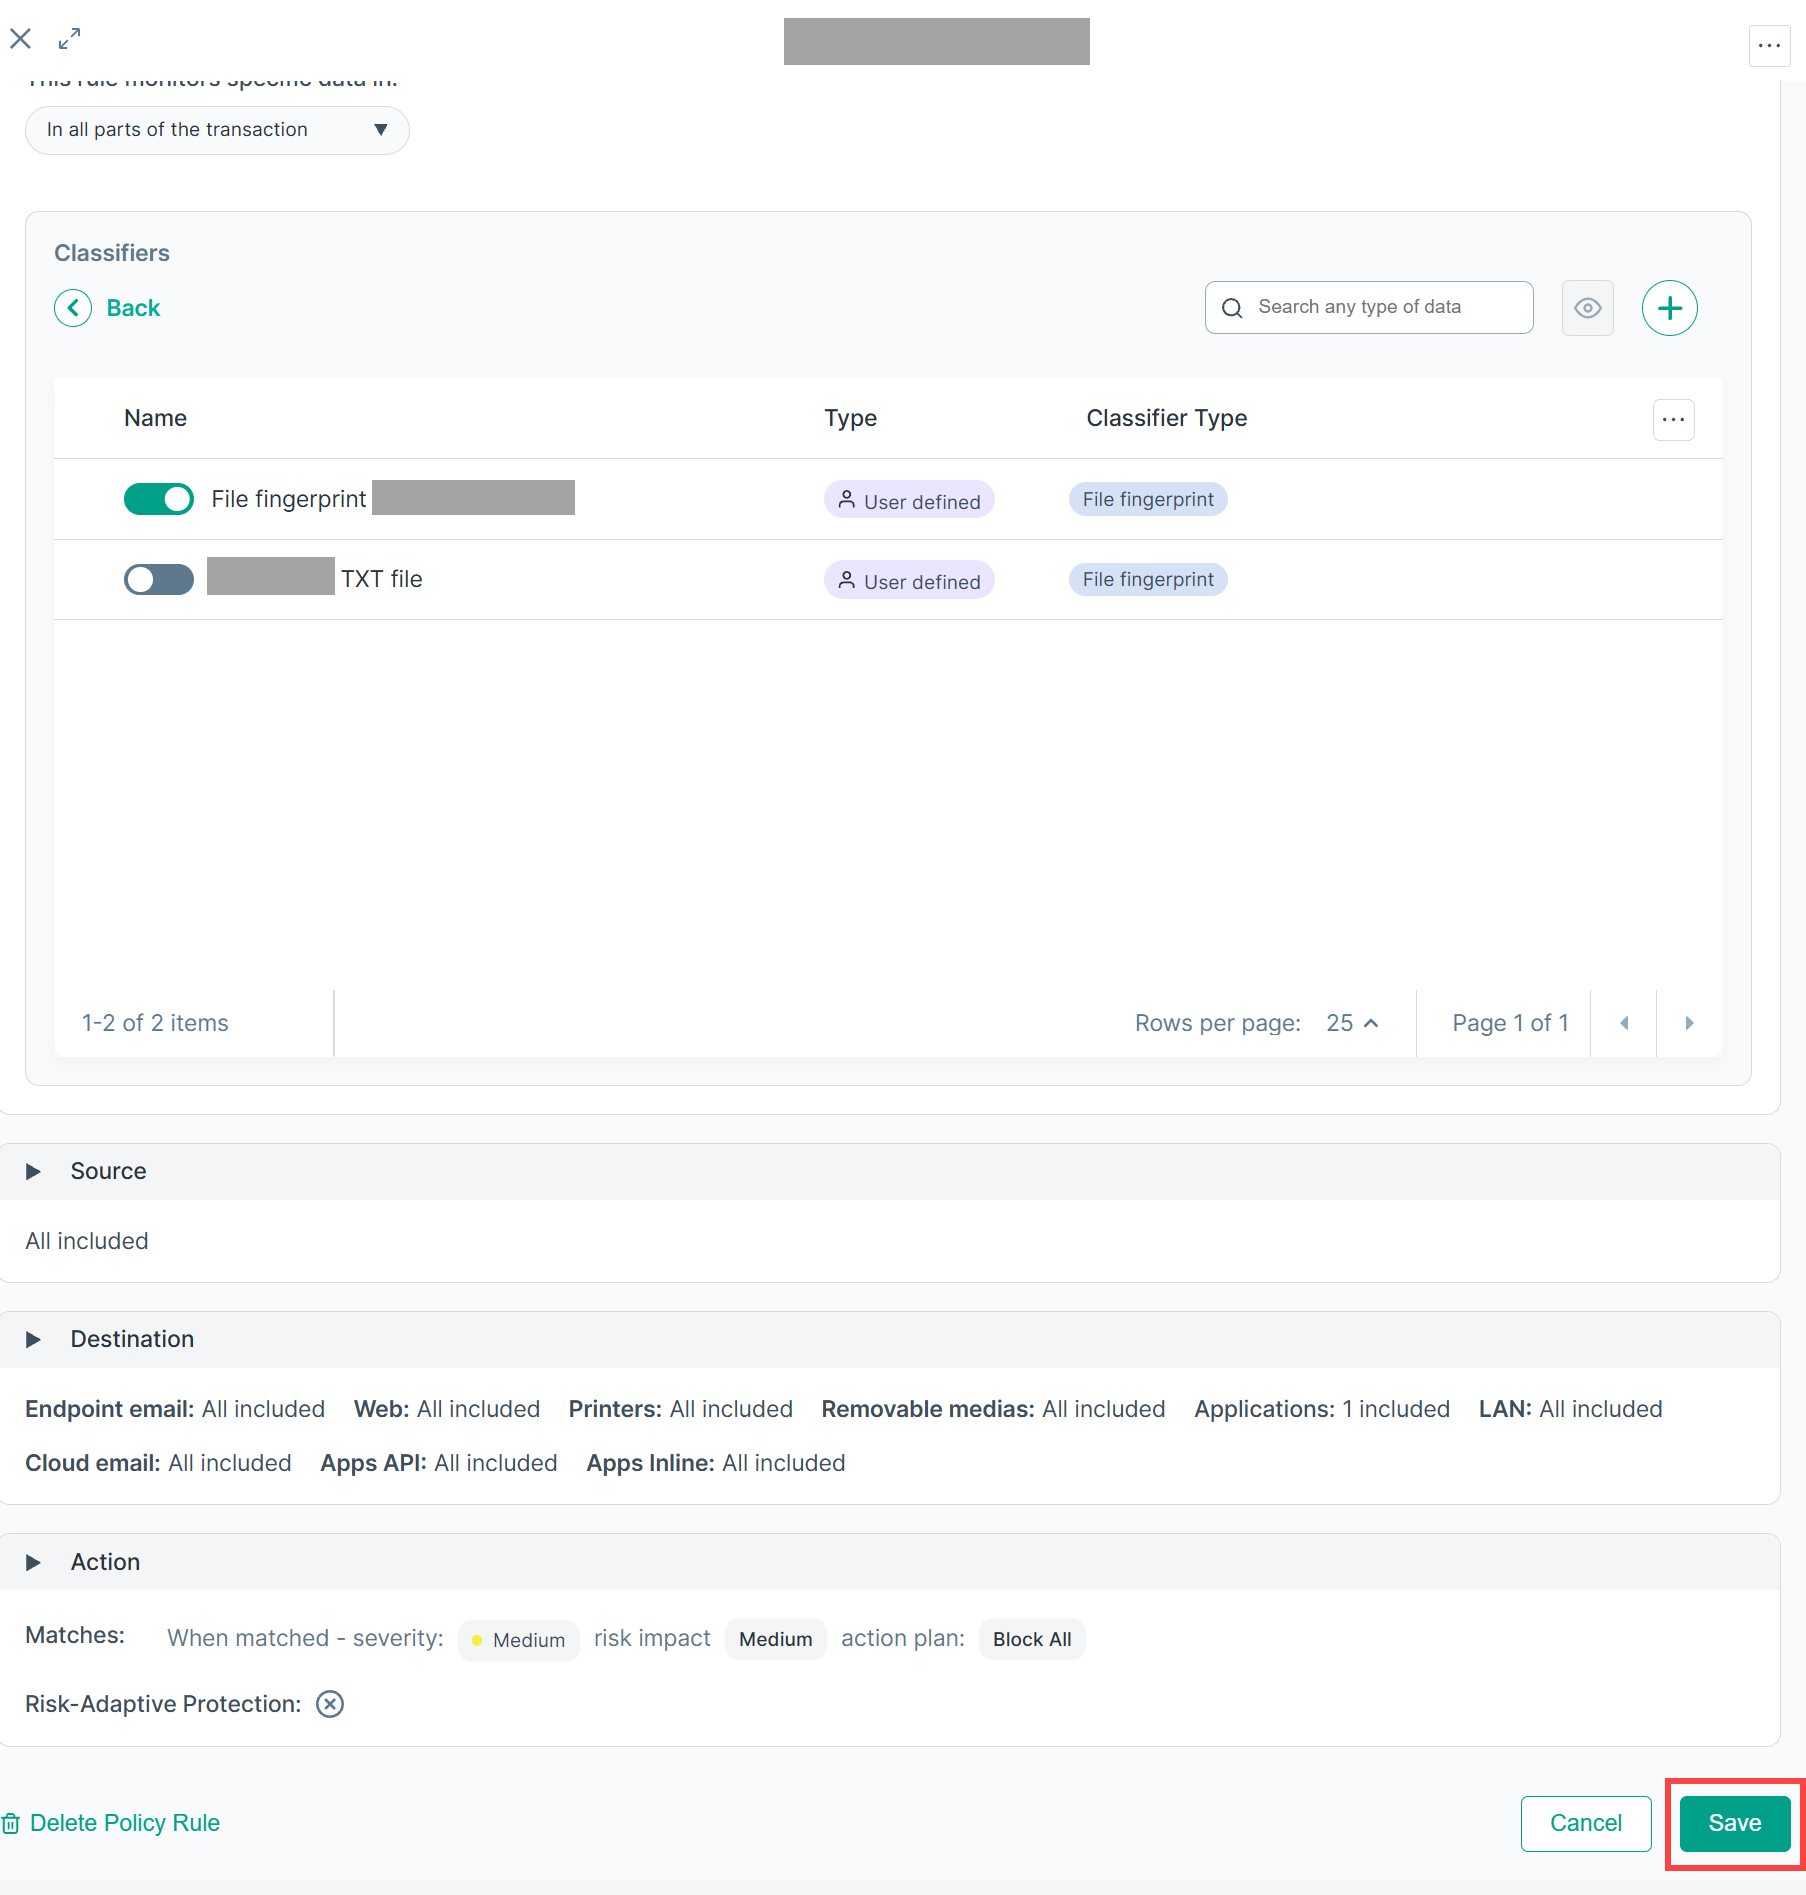
- Save the rule.
- The Forcepoint Data Security Cloud | DLP now matches content against the fingerprinted file or directory as part of policy evaluation.