NetApp ONTAP
The NetApp ONTAP connector discovers, scans, classifies, and remediates data stored on ONTAP Storage Virtual Machines (SVMs) for on-premises DSPM deployments.
This topic describes the architecture, prerequisites, configuration, scanning workflow, capabilities, and operational notes for the NetApp ONTAP connector.
Architectural Overview
The NetApp ONTAP connector discovers, scans, classifies, and remediates data stored on ONTAP Storage Virtual Machines (SVMs) for on-premises DSPM deployments.
The connector operates using a dual-channel architecture against the same SVM. Both communication channels must be reachable from the DSPM scanner for a scan to complete successfully:
- ONTAP REST API channel (SVM management LIF) — used for discovery, file and folder enumeration, metadata retrieval, permission read/write, trustee enumeration, and audit log reading.
- CIFS/SMB share channel (SVM CIFS data LIF) — used for retrieving file content for classification, applying persistent (hard) tags, and executing file move operations.
Both NTFS and UNIX security-style volumes are fully supported. Data content across both security styles is accessed strictly over the CIFS share; an NFS client data path is not used.
Prerequisites and System Requirements
Network Reachability
The following ports and endpoints must be open between the DSPM scanner and the SVM:
| Channel | Endpoint | Default Port | Purpose |
|---|---|---|---|
| ONTAP REST API | SVM management LIF | TCP 443 (HTTPS) |
Discovery, metadata, permissions, trustees |
| CIFS/SMB | SVM CIFS data LIF | TCP 445 (SMB) |
Content retrieval, hard tagging, move-file |
ONTAP Version
Minimum supported version: ONTAP 9.10.1 or higher.
Required SVM REST API Privileges
The connector authenticates using an SVM-scoped account. Create a custom role on the SVM that grants access to the REST endpoints listed below.
| Access | API Path | Purpose |
|---|---|---|
| readonly | /api/cluster | Connection testing |
| readonly | /api/cluster/jobs | Polling asynchronous ACL jobs to completion |
| readonly | /api/svm/svms | SVM discovery |
| all | /api/storage/volumes | Volume discovery, file and folder enumeration, file metadata, deletion, and reading NAS audit logs |
| readonly | /api/protocols/cifs/shares | Mapping volume paths to CIFS shares |
| readonly | /api/protocols/cifs/services | Querying CIFS server settings (default UNIX user, AD domain) |
| readonly | /api/protocols/cifs/local-users | Enumerating CIFS local user trustees |
| readonly | /api/protocols/cifs/local-groups | Enumerating CIFS local group trustees |
| readonly | /api/name-services/unix-users | Enumerating UNIX user trustees |
| readonly | /api/name-services/unix-groups | Enumerating UNIX group trustees and memberships |
| all | /api/protocols/file-security/permissions | Reading DACLs; adding, trimming, or removing ACEs during remediation |
| readonly | /api/protocols/file-security/effective-permissions | Evaluating effective permissions |
| readonly | /api/security/accounts | Verifying the connector's own role privileges |
| readonly | /api/protocols/audit | Optional. Querying NAS audit configuration for temporal trustee fields |
Storage and Permission Requirements
CIFS share exposure. Every volume in scope must be exposed through a CIFS share. Volumes that are visible over REST without a corresponding CIFS share will be discovered, but their file content will not be classified.
Root ACE permissions (NTFS volumes). An explicit ACE granting modify-equivalent rights must be configured for the CIFS scan account at the root of every NTFS volume, applied to this folder, subfolders, and files:
| Right | Required For |
|---|---|
write_data, append_data |
Stub creation and persistent tagging |
write_attr, write_ea |
Tag metadata |
delete (applied to files) |
File move and rename operations |
Connection Configuration and Identity Backing
Creating the Connection in DSPM
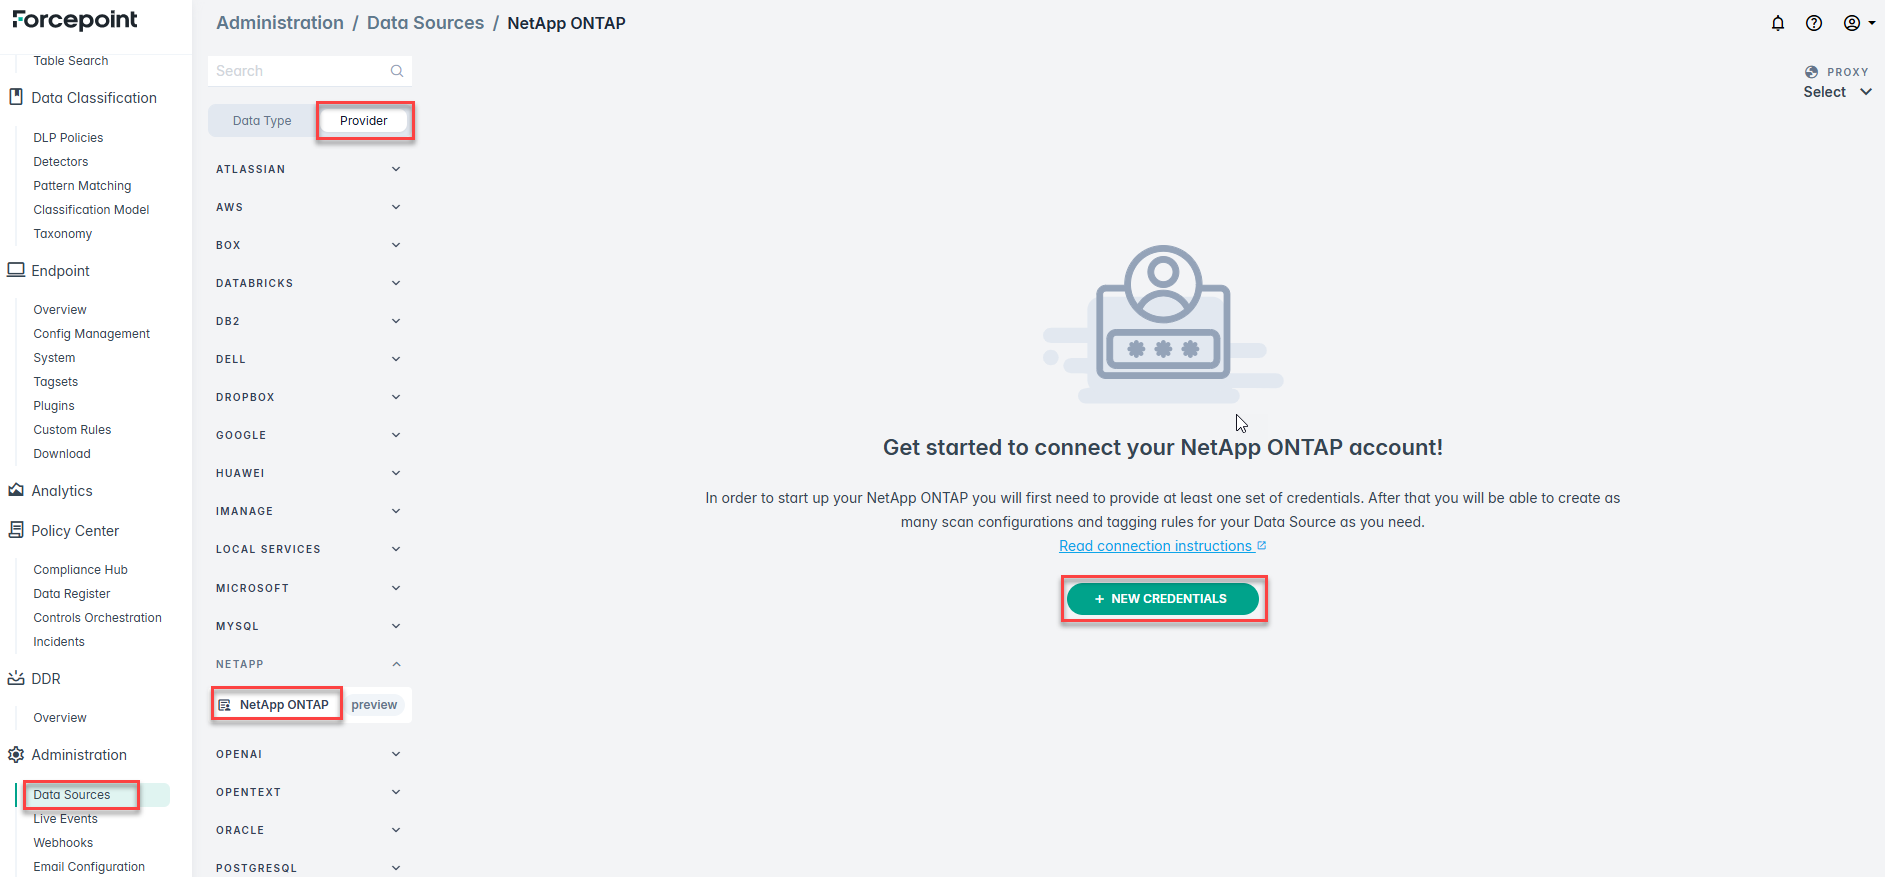
In the DSPM console, navigate to , switch to the Provider tab, expand NETAPP, and select NetApp ONTAP. Because no credentials exist yet, the connector opens on its start page; choose + NEW CREDENTIALS to define the first credential set. Once at least one credential set is saved, scan configurations and tagging rules can be created against it.
Figure: Figure 1: Selecting the NetApp ONTAP provider under Administration > Data Sources and starting a new credential set.
Credentials Required
To configure the NetApp ONTAP connection in DSPM, provide:
- ONTAP management endpoint / SVM LIF — REST API host or IP address.
- SVM-scoped API user and password — REST credentials matching the role defined in Required SVM REST API Privileges.
- CIFS/SMB user and password — scan account for data access over SMB.
- SMB domain — required for Active Directory-backed SVMs to qualify the CIFS scan account.
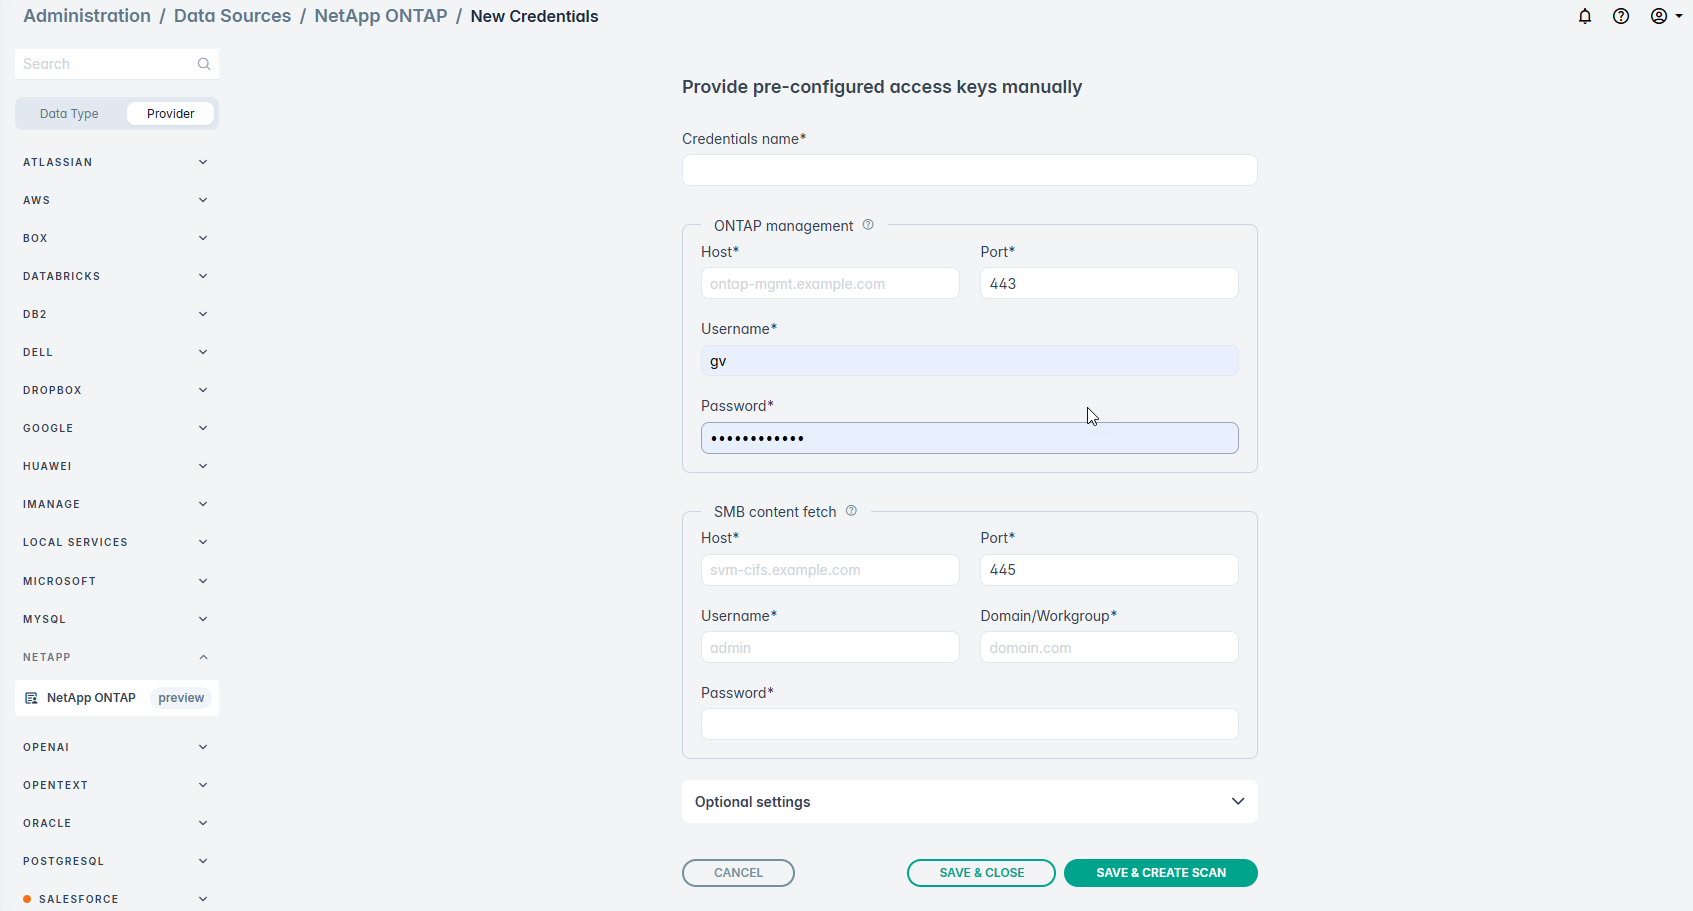
The credentials form is split into two groups that correspond directly to the two communication channels described in Architectural Overview. ONTAP management takes the SVM management LIF host and port (443 by default) with the SVM-scoped REST account, while SMB content fetch takes the CIFS data LIF host and port (445 by default) with the scan account and its domain or workgroup. Both groups are mandatory — omitting the SMB details leaves content classification, persistent tagging, and file moves unavailable. Use SAVE & CLOSE to store the credentials, or SAVE & CREATE SCAN to continue straight into a scan configuration.
Figure: Figure 2: New Credentials form — the ONTAP management (REST) and SMB content fetch (CIFS) channels are configured separately.
Identity Models
Workgroup-backed SVM. Resolves local CIFS users and groups, and UNIX users and groups, directly from ONTAP local tables.
Active Directory-backed (domain-joined) SVM. Domain principals are mapped to join trustees discovered by the DSPM LDAP/AD connector. An active LDAP/AD connector covering the same domain must be configured in DSPM for domain trustees to resolve properly.
Scanning and Verifying Results
With credentials in place, a scan configuration defines what the connector reads and how much of the SVM it covers.
Creating a Scan Configuration
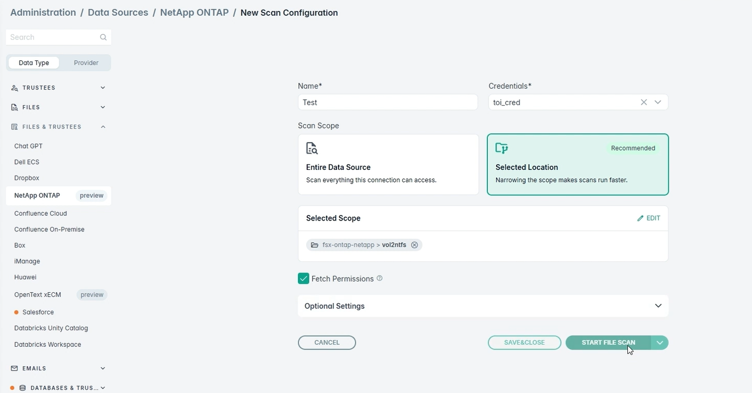
Give the configuration a name and select the saved credential set. For Scan Scope, either Entire Data Source covers everything the connection can reach, or Selected Location narrows the scan to specific SVM volumes — the recommended option, since a tighter scope completes noticeably faster. Enabling Fetch Permissions instructs the connector to read DACLs and enumerate trustees over the REST channel using the privileges listed in Required SVM REST API Privileges. START FILE SCAN queues the scan immediately.
Figure: Figure 3: Scan configuration with the scope narrowed to a single volume and permission fetching enabled.
Monitoring Scan Progress
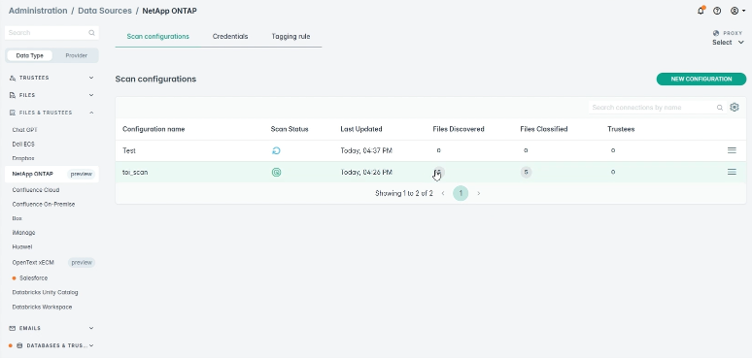
The connector page lists every configuration on the Scan configurations tab, with live scan status, last-updated time, and running counts of files discovered, files classified, and trustees resolved. A rising discovered count with classified remaining at zero is the usual signature of an unreachable CIFS data LIF, because enumeration runs over REST while content retrieval requires SMB. The adjacent Credentials and Tagging rule tabs manage the stored credential sets and the rules that drive persistent tagging.
Figure: Figure 4: Scan configurations list showing scan status and discovery, classification, and trustee counts.
Reviewing Classified Files
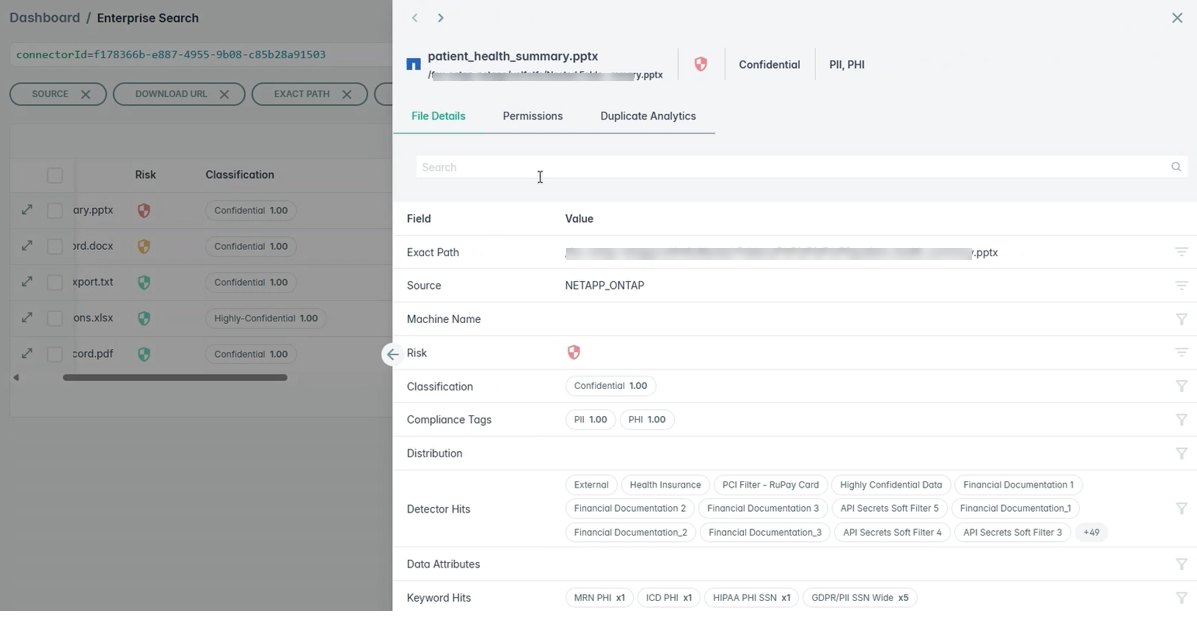
Completed results are available in Enterprise Search, where each file can be opened for detail. The Source field reports NETAPP_ONTAP, confirming the origin, alongside risk, classification and confidence, compliance tags such as PII and PHI, detector hits, and keyword hits. The Permissions tab exposes the trustee data collected when Fetch Permissions is enabled, and is the starting point for the remediation actions summarised in Capabilities and Limitations Matrix.
Figure: Figure 5: Enterprise Search file details for a file scanned from NetApp ONTAP, including classification and compliance tags.
Capabilities and Limitations Matrix
| Feature / Action | NTFS Security Style | UNIX Security Style |
|---|---|---|
| Discovery and file enumeration | Supported | Supported |
| Content scanning and classification | Supported | Supported |
| Permission and trustee reading | Supported | Supported |
| Move file remediation | Supported | Supported |
| Revoke permissions remediation | Supported | Not supported (ONTAP API restriction) |
| Persistent (hard) tagging | Supported | Supported |
| Soft / cloud tagging | Not supported | Not supported |
| MIP / AIP tagging | Not supported | Not supported |
| Event / extended streaming | Not supported | Not supported |
| Third-party pre-existing labels | Not supported | Not supported |
Key Implementation Details
Permission revocation. Revoking permissions on UNIX files fails because of ONTAP REST API restrictions on UNIX mode-bit and ACL modifications, regardless of the scan account's privilege level.
Tagging. Only hard (persistent) tagging embedded directly into the file structure is supported. Cloud-based soft tagging and Microsoft Information Protection (MIP) tags are not supported.
NFS access. NFS client data access is not implemented; all file content retrieval runs over SMB.
Operational Notes: Temporal Trustee Fields
To populate temporal trustee fields — such as account creation, password modification, and last login dates — NAS auditing must be enabled on the target SVM:
- Required audit categories:
cifs_logon_logoffanduser_account. - Audit log output format must be set to XML (
-format xml).